MITRE ATT&CK: Basic Concepts and Best Practices
MITRE ATT&CK is a globally-accessible knowledge base of adversary tactics and techniques based on real-world observations.
What Is MITRE ATT&CK?
MITRE ATT&CK is a knowledge base of adversary tactics and techniques based on real-world observations. The framework provides a common language and understanding of adversary behavior, which can help organizations defend against potential cyber attacks, and improve their overall security posture.
ATT&CK is maintained by MITRE, a non-profit organization that operates research and development centers for the U.S. government. It provides systems engineering, research and development, and IT support to various agencies, including the Department of Defense, the Federal Aviation Administration, and the Department of Veterans Affairs.
MITRE’s mission is to solve problems of national importance by bringing the best of science, engineering, and technology to bear on the challenges faced by the government.
This is part of a series of articles about vulnerability management.
In this article:
What Are MITRE ATT&CK Tactics and Techniques?
MITRE ATT&CK tactics and techniques are categories and specific actions used by adversaries to achieve their objectives in a cyber attack. The tactics represent the overarching goals of the attacker, while the techniques represent the specific actions taken to achieve those goals.
The tactics in MITRE ATT&CK include:
- Initial access: Techniques used to gain initial access to a target system or network.
- Execution: Techniques used to run malicious code or payloads on a target system.
- Persistence: Techniques used to maintain access and control over a target system.
- Privilege escalation: Techniques used to increase privileges on a target system.
- Defense evasion: Techniques used to evade or bypass security controls and hide malicious activity.
- Credential access: Techniques used to steal or obtain valid credentials from a target system.
- Discovery: Techniques used to gather information about a target system or network.
- Lateral movement: Techniques used to move from one system to another within a target network.
- Collection: Techniques used to gather information from a target system.
- Command and control: Techniques used to maintain communication and control over a compromised system.
- Exfiltration: Techniques used to extract data or information from a target system.
- Impact: Techniques used to cause harm to a target system or organization.
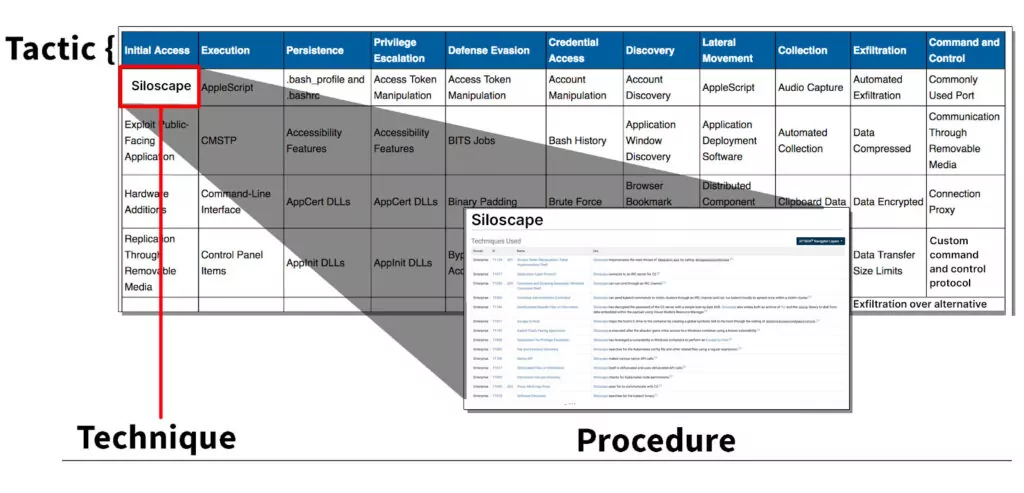
The techniques within each tactic are continually updated and expanded as new observations of adversary behavior become available. For each technique, MITRE provides several procedures that explain specific ways attackers use the technique and how to defend against it.
The following image illustrates the relationship between tactics, techniques, and procedures in the MITRE ATT&CK Framework.
What Is Included in the MITRE ATT&CK Matrix?
The MITRE ATT&CK matrix is a visual representation of the tactics and techniques used by adversaries in cyber attacks. The matrix provides a comprehensive overview of the different stages of an attack and the specific tactics and techniques used at each stage. Each cell in the matrix represents a specific technique and is color-coded to indicate the platforms and operating systems on which the technique has been observed.
The matrix is organized into columns, which represent the tactics, and rows, which represent the techniques. The matrix also includes information on the data sources and references used to validate each technique, as well as the platforms and operating systems on which the technique has been observed.
MITRE ATT&CK includes several different matrices that focus on specific platforms, operating systems, and threat actor groups:
- Enterprise Matrix: The primary matrix that covers tactics and techniques used against enterprise targets. It also includes the Containers Matrix which covers tactics and techniques for containerized environments.
- Mobile Matrix: A matrix that focuses on tactics and techniques used against mobile devices.
- ICS Matrix: A matrix that focuses on tactics and techniques used against Industrial Control Systems.
The matrices are a valuable resource for security professionals, providing a clear and concise overview of adversary behavior and can be used to inform security planning, testing, and response efforts. They are continuously updated and expanded as new observations of adversary behavior become available.
Best Practices For Using MITRE ATT&CK
Here are some best practices for using MITRE ATT&CK:
- Understand your threat landscape: Before using ATT&CK, it’s important to understand the types of threats your organization is likely to face, and what your organization’s specific risk tolerance is. This will help you identify which tactics and techniques are most relevant to your organization, and prioritize your defense efforts accordingly.
- Use the matrix to identify gaps in your defenses: The ATT&CK matrix is a useful tool for identifying gaps in your organization’s defenses. By mapping out the different stages of an attack and the techniques that can be used at each stage, you can identify areas where your organization may be vulnerable and take steps to improve your defenses.
- Use the techniques as a starting point for detecting threats: The techniques in the ATT&CK matrix can be used as a starting point for detecting threats. By understanding the specific methods and tools that adversaries are likely to use, you can create more targeted detection and response capabilities.
- Use the matrix to improve incident response: The ATT&CK matrix can also be used to improve incident response capabilities. By understanding the different stages of an attack and the techniques that can be used at each stage, you can create more effective incident response plans and procedures.
- Use the matrix to inform security investments: Use the matrix to inform security investments. By understanding the tactics and techniques used by adversaries, you can make more informed decisions about where to invest in security technologies and services.
- Continuously monitor and update: The matrix is a living document, and new tactics and techniques are added regularly. It’s important to continuously monitor the matrix and update your organization’s defenses accordingly.
- Share and collaborate: Share the knowledge with your team, partners and other organizations. Collaborate with other organizations to share information about tactics, techniques, and tools used by adversaries, to improve the overall security posture.
Learn more About Vulnerability Management
Open Source Vulnerability Scanning: Methods and Top 5 Tools
Open source vulnerability scanners, often used as part of Software Composition Analysis (SCA) tools, are used to detect open source components used in software projects, and check if they contain unpatched security vulnerabilities, and help organizations remediate them. These tools scan complex dependency trees, because vulnerabilities can be found in a dependent library used by the main component or brought into an application during the build phase. Learn how open source vulnerability scanning works and discover tools that can help you identify and remediate vulnerabilities in OSS components and containers.
Read more: Open Source Vulnerability Scanning: Methods and Top 5 Tools
Trivy Vulnerability Scanner Adopted by Leading Cloud Native Platforms
Trivy is a comprehensive and easy-to-use open source vulnerability scanner for container images. Unlike other open source scanners, Trivy covers both OS packages and language-specific dependencies and is extremely easy to integrate into organizations’ software development pipelines. Trivy vulnerability scanner is being added as an integrated option in the CNCF’s Harbor registry, in GitLab, and in Mirantis Docker Enterprise.
Read more: Trivy Vulnerability Scanner Adopted by Leading Cloud Native Platforms
Aqua Cloud Native Application Protection Platform (CNAPP)
Go cloud native with the experts!