Monitor
Scan source code, open source dependencies, IaC and pipeline configuration for vulnerabilities, secrets, misconfigurations and malware, including secrets buried in commit history.
Explore MonitorIdentify where each artifact came from and who owns it, so teams can trace production findings back to the source and prove supply chain integrity to auditors.
Scan source code, open source dependencies, IaC and pipeline configuration for vulnerabilities, secrets, misconfigurations and malware, including secrets buried in commit history.
Explore MonitorTrace a vulnerability found in production back to the image, repository, pipeline, commit and owner involved, so the right team fixes the source while runtime controls protect the application.
Explore DetectGenerate and validate SBOMs in SPDX and CycloneDX formats and support SLSA provenance, so teams can show where every artifact came from.
Explore ComplianceCatch vulnerable and risky components before they ship. Aqua Trivy scans source repositories and open source dependencies for known vulnerabilities and flags license risk alongside each finding.
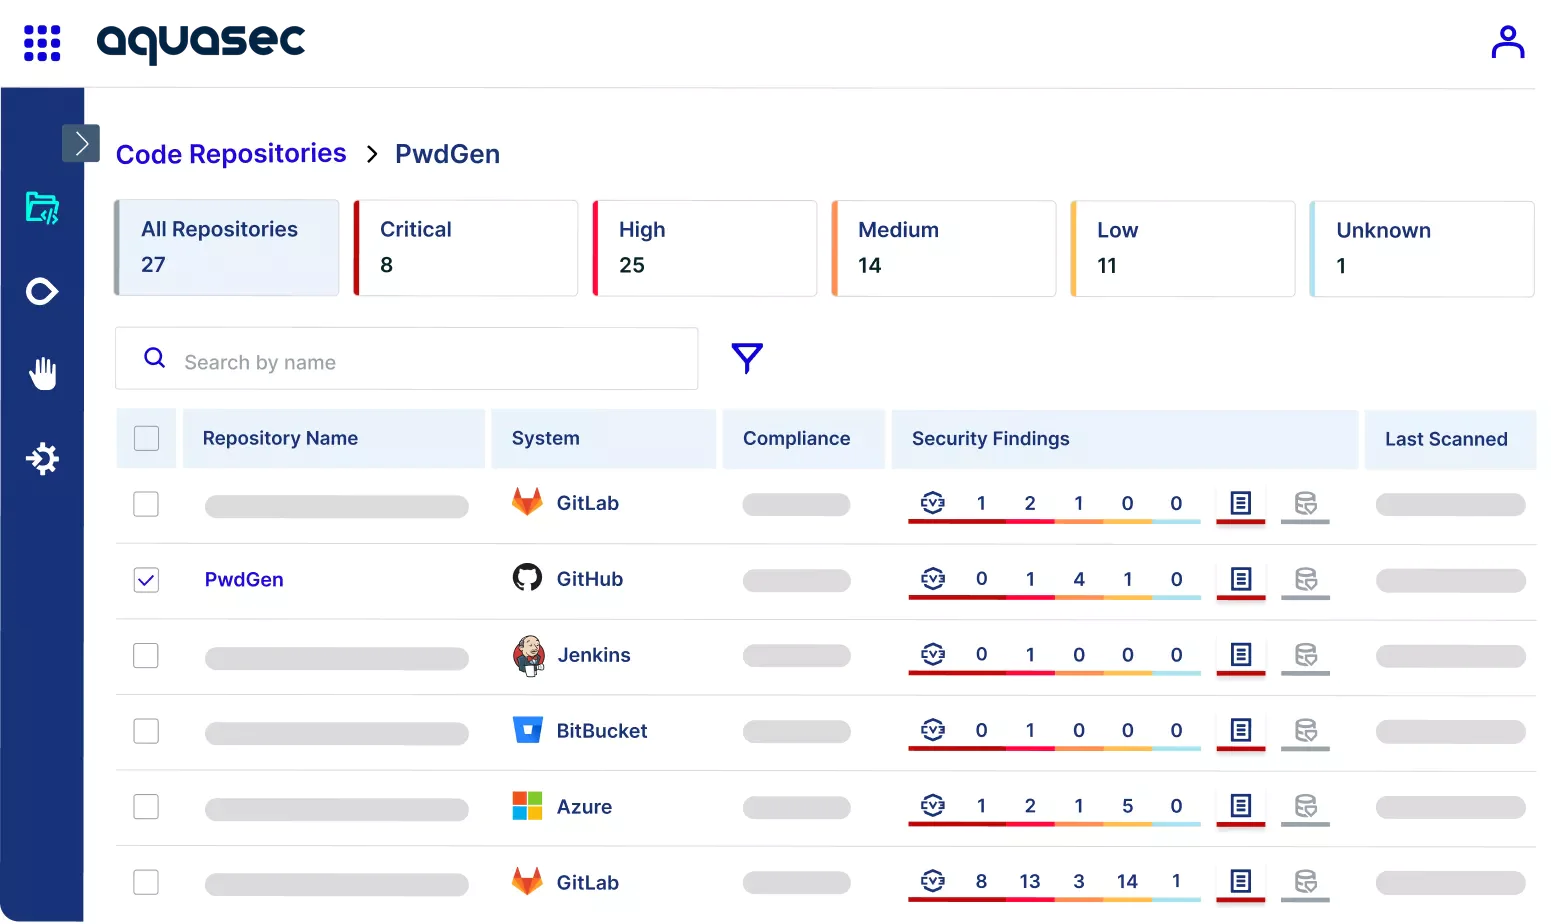
Fix cloud and Kubernetes misconfigurations while they are still in code. Aqua scans infrastructure as code, including Kubernetes manifests and Dockerfiles, for misconfigurations and embedded secrets.
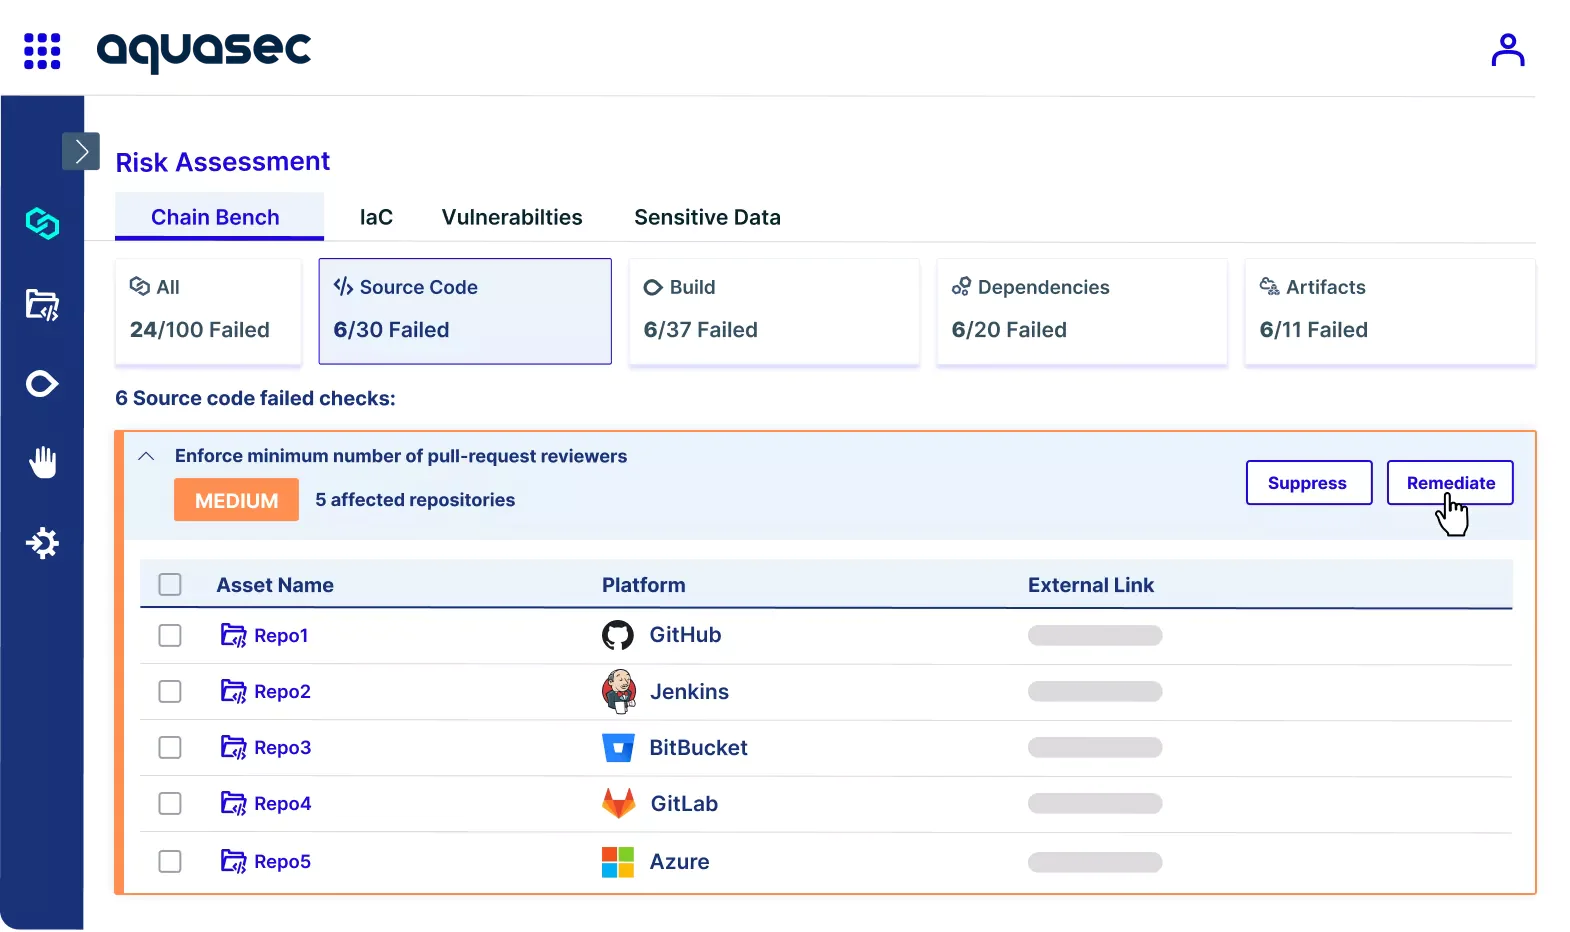
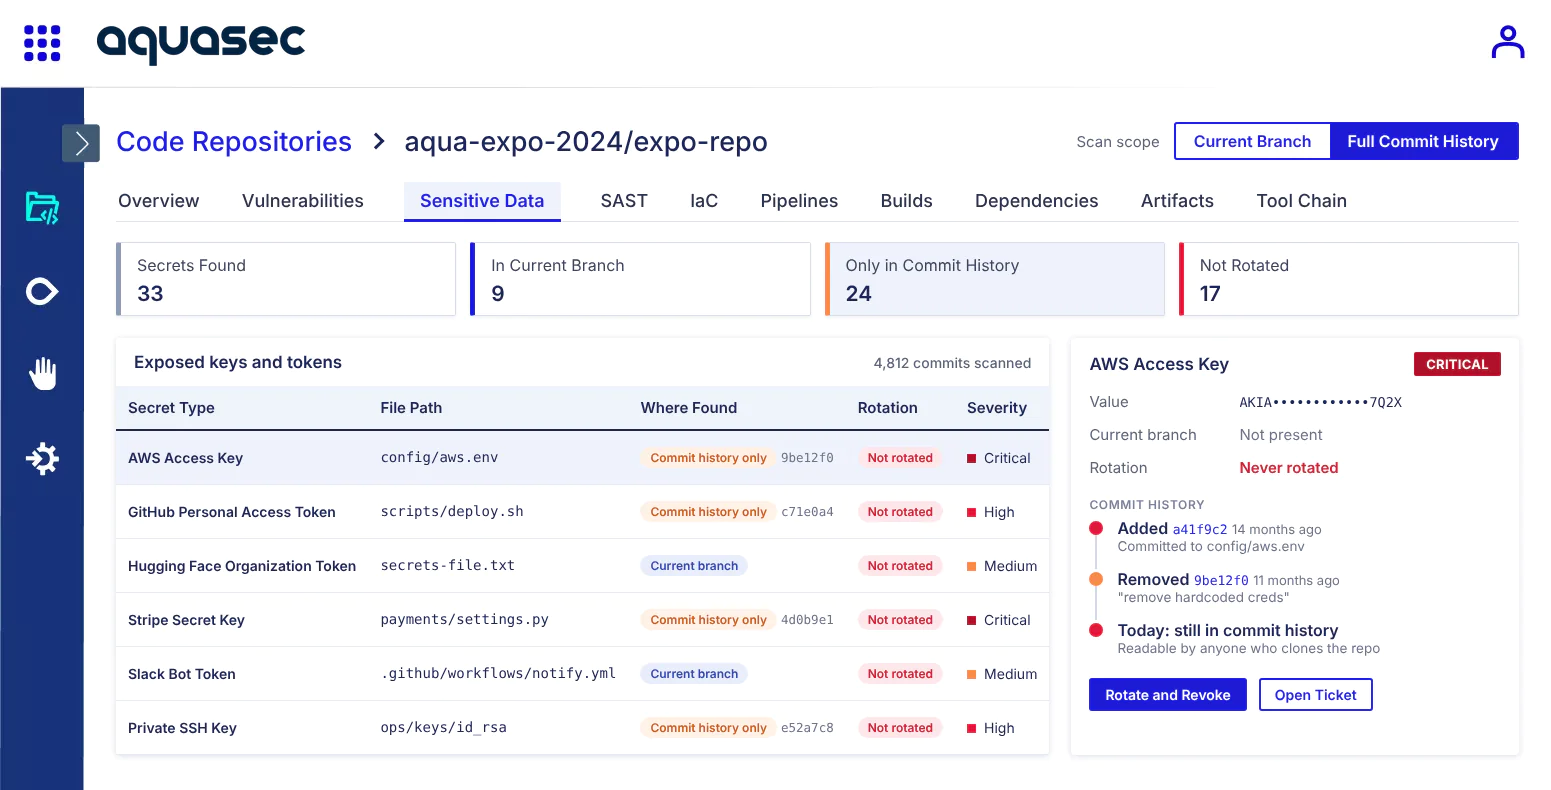
Close exposure from credentials that were removed from code but never rotated. Aqua scans repositories and their full commit history for exposed keys and tokens, including secrets that no longer appear in the current branch.
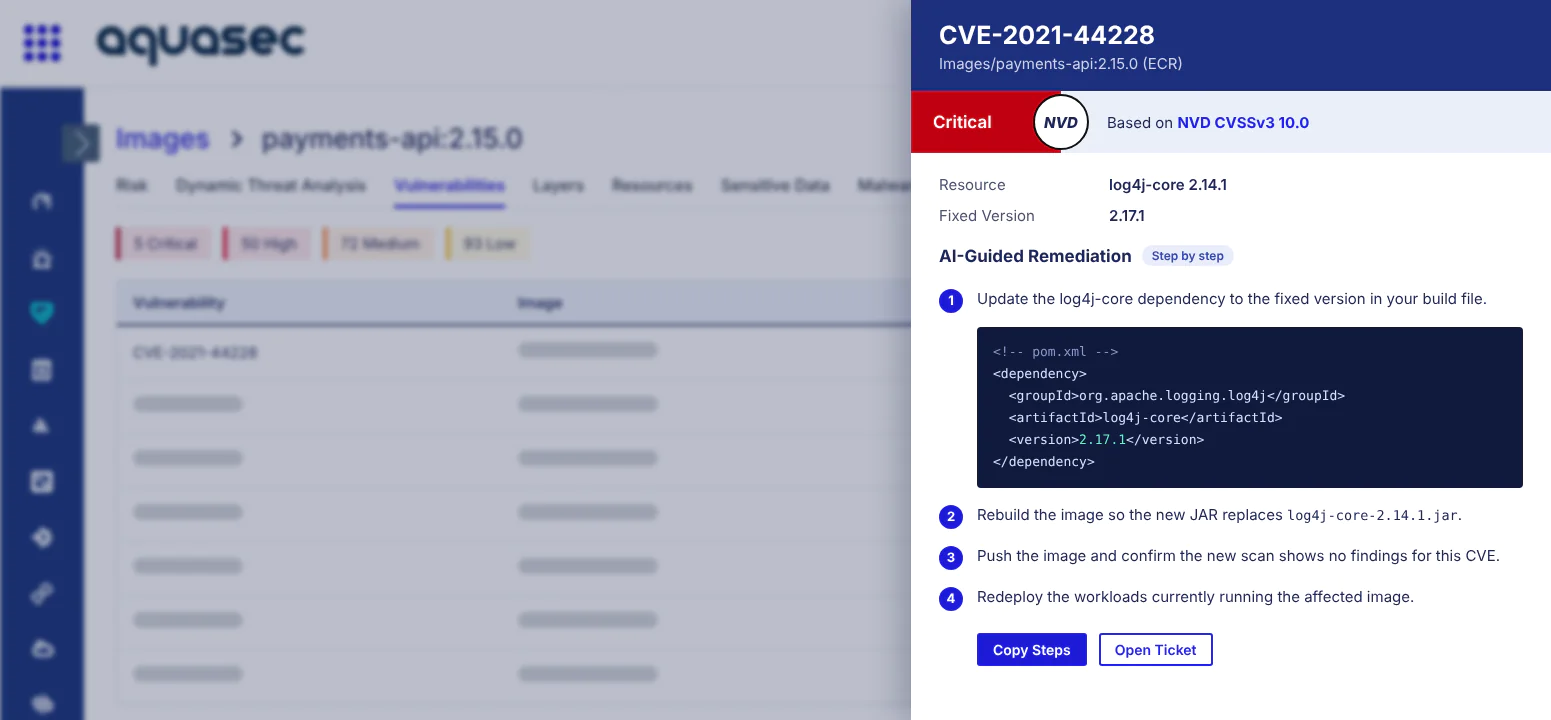
Help developers fix issues without leaving their workflow. Aqua delivers findings in the IDE, in pull request comments, in CI pipelines and in source repositories, with remediation guidance attached.
Keep attackers from tampering with the path from commit to artifact. Aqua analyzes CI/CD configuration in tools such as GitHub Actions, GitLab CI, Jenkins and Azure Pipelines for misconfigurations and applies integrity controls so only intended code reaches production.
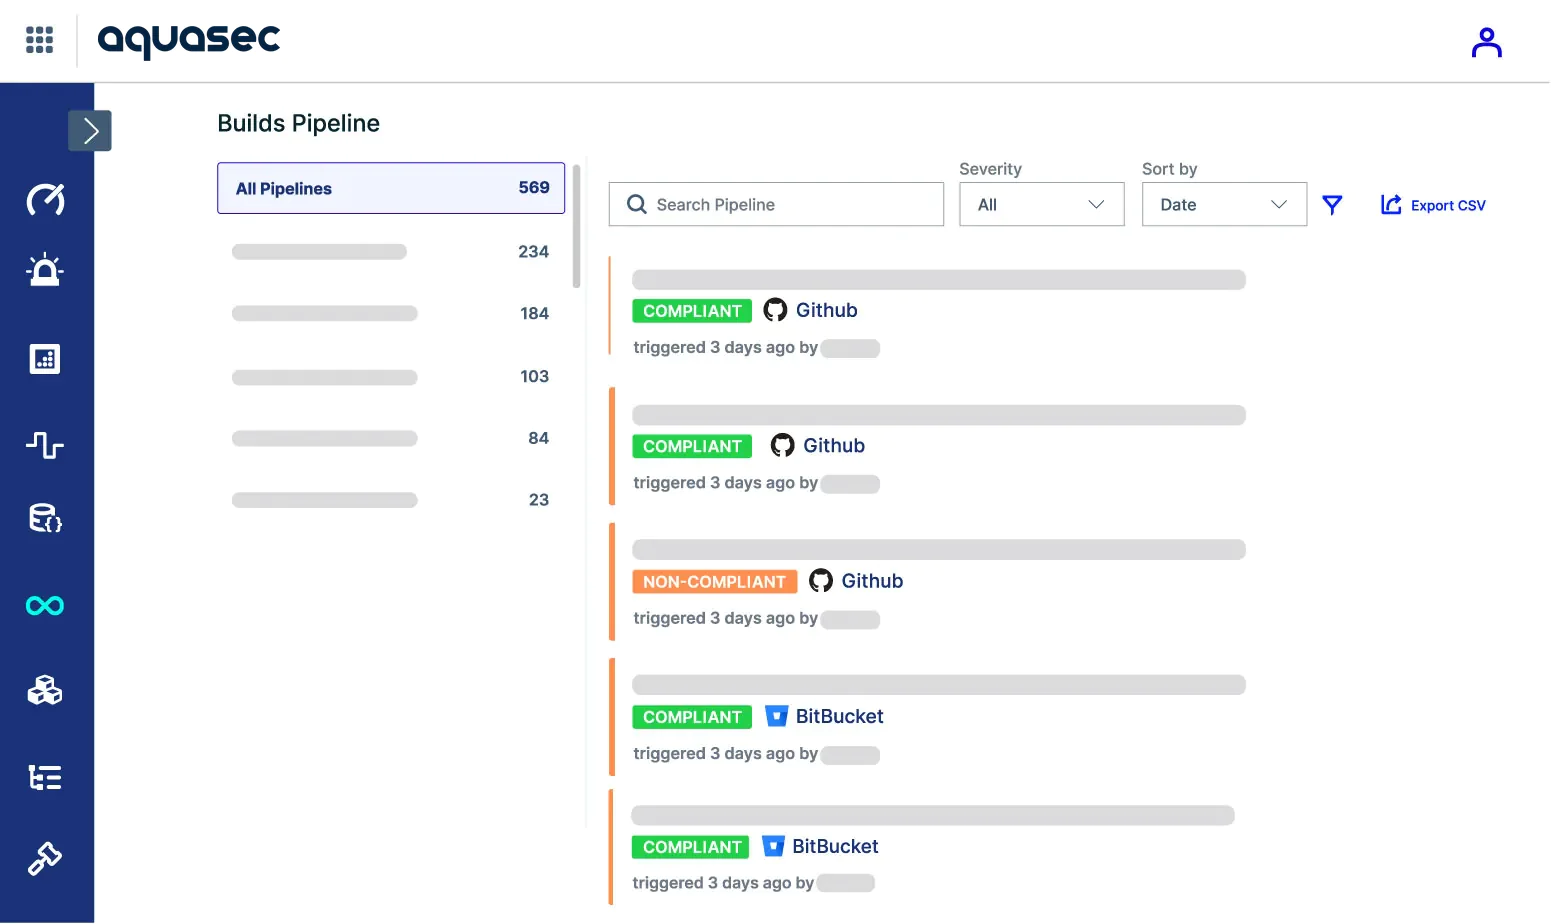
Answer what is inside a release and how it was built. Aqua generates SBOMs for each artifact and supports SLSA provenance, giving runtime protection and auditors the same record of what was intended to run.
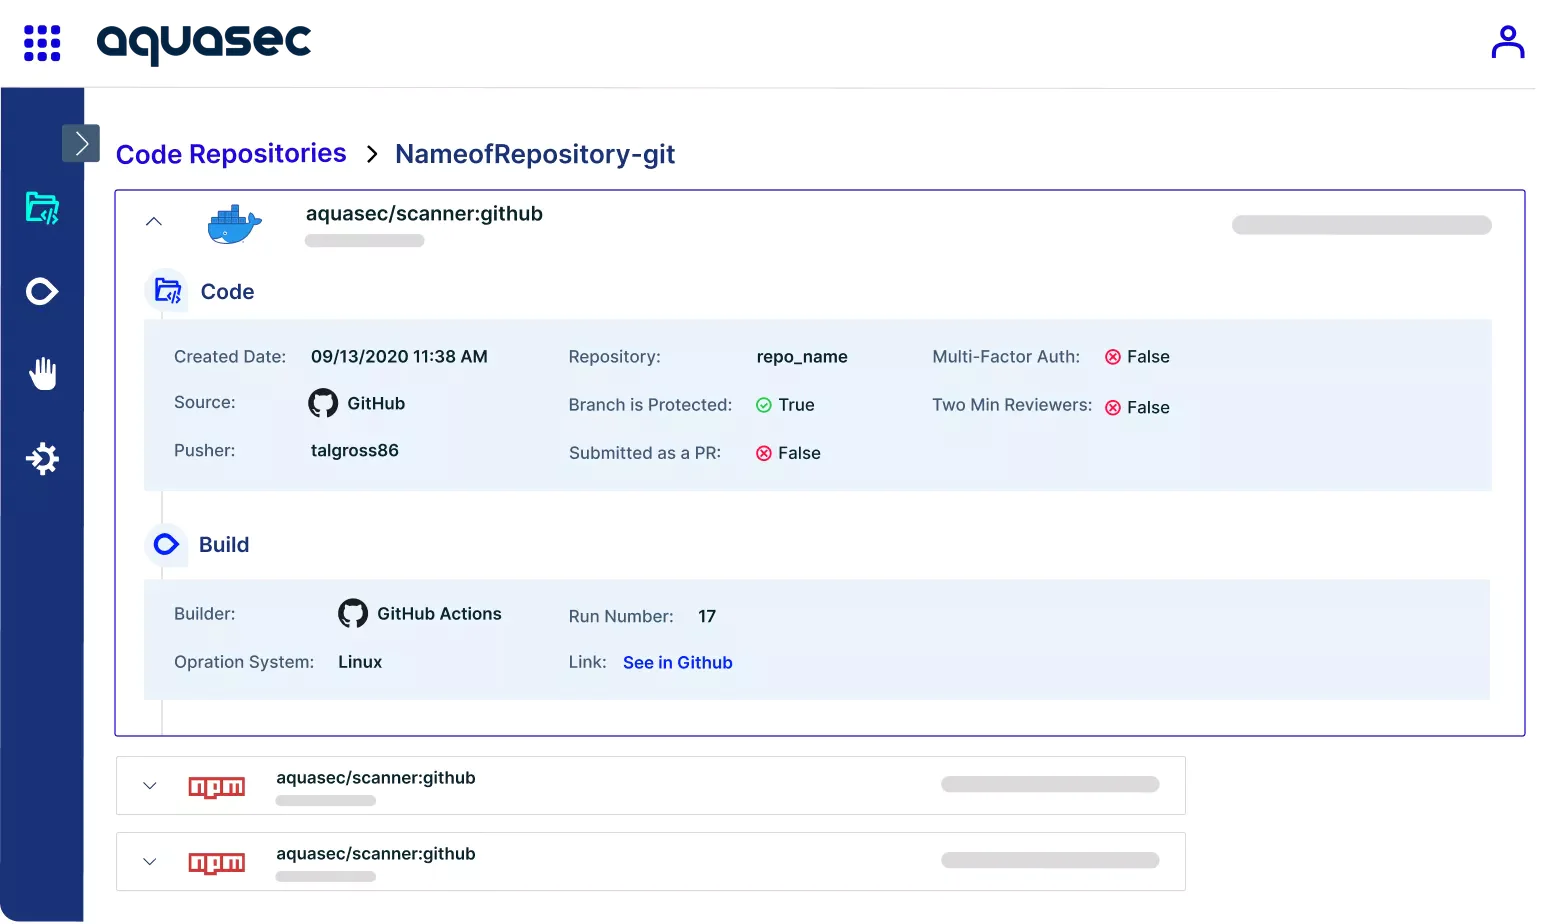
Code Security connects to source control and CI/CD systems, then routes findings to the workflow tools teams use to fix them.
 GitLab
Automate container image scanning in GitLab CI/CD pipelines to empower DevOps to detect and fix security issues early, and accelerate application deployment.
Read the GitLab Case Study
 Jenkins
Automate container image scanning in Jenkins CI/CD pipelines to empower DevOps to detect and fix security issues early, and accelerate application deployment.
Learn More
 Atlassian Jira
Automatically open tickets for vulnerabilities and security issues discovered by Aqua, to enable rapid remediation by DevOps teams.
Learn More
 Azure DevOps
Scan images and functions directly in Azure DevOps CI/CD pipelines to empower DevOps to detect and fix security issues early, and accelerate application deployment.
Get Aqua for Azure DevOps
Code security finds and fixes security issues in source code, open source dependencies, infrastructure as code and build pipelines before software reaches production. Aquasec adds traceability from each finding to its repository, commit and owner, and connects that record to runtime protection.
A standalone scanner reports what is wrong in code. Aquasec connects code findings to what actually runs, tracing production vulnerabilities back to the commit and owner that introduced them, so runtime protection knows what each workload was intended to run.
Aquasec analyzes open source dependencies, infrastructure as code, secrets and security relevant source patterns, but it is not a comprehensive SAST or DAST platform for proprietary application code. It works alongside existing application testing tools.
Historical secret scanning checks a repository’s full commit history, not only the current code, for exposed credentials. A key deleted from the latest commit still lives in history and can still be used, so Aquasec flags it for rotation.
Yes. Aquasec generates and validates SBOMs in standard formats such as SPDX and CycloneDX and supports SLSA provenance, giving teams a record of what each artifact contains and how it was built.
See runtime control stop an attack the moment it tries to execute.