Sensitive Workloads Require Proven Security
Organizations handling sensitive government data need security technology that meets rigorous federal requirements and can protect workloads across cloud, on premises and air gapped environments.
Cloud environments continue to change after an assessment. Without continuous monitoring, enforcement and evidence, organizations can fall out of alignment long before the next audit.
Organizations handling sensitive government data need security technology that meets rigorous federal requirements and can protect workloads across cloud, on premises and air gapped environments.
Vulnerability counts and severity scores cannot tell leaders what security risk could cost the business or how much enforced controls reduce that exposure.
Control data is often spread across separate tools and teams, creating a time consuming effort to prove which policies were applied and whether they remained effective.
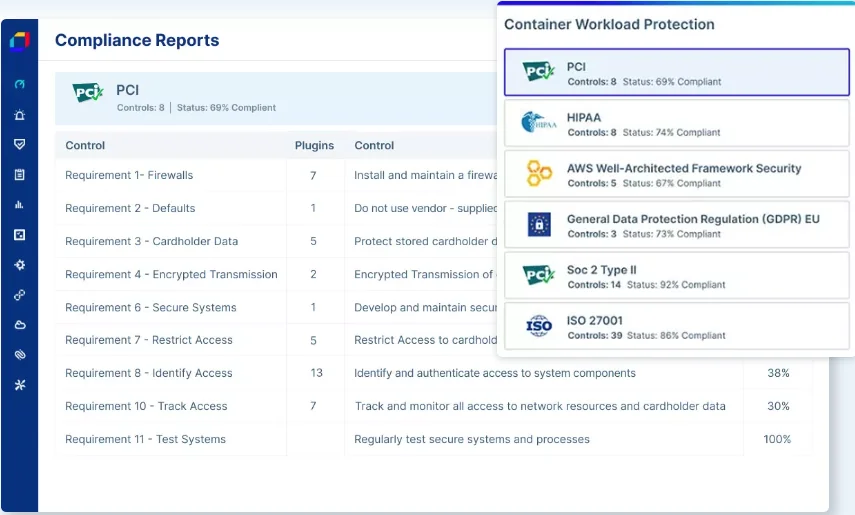
Translate compliance requirements into security controls, enforce policy across the application lifecycle and keep evidence ready for audits.

Address technical controls and evidence requirements across FedRAMP, DORA, NIST, PCI DSS, HIPAA, GDPR, SOC 2 and CIS Benchmarks while identifying gaps as environments change.
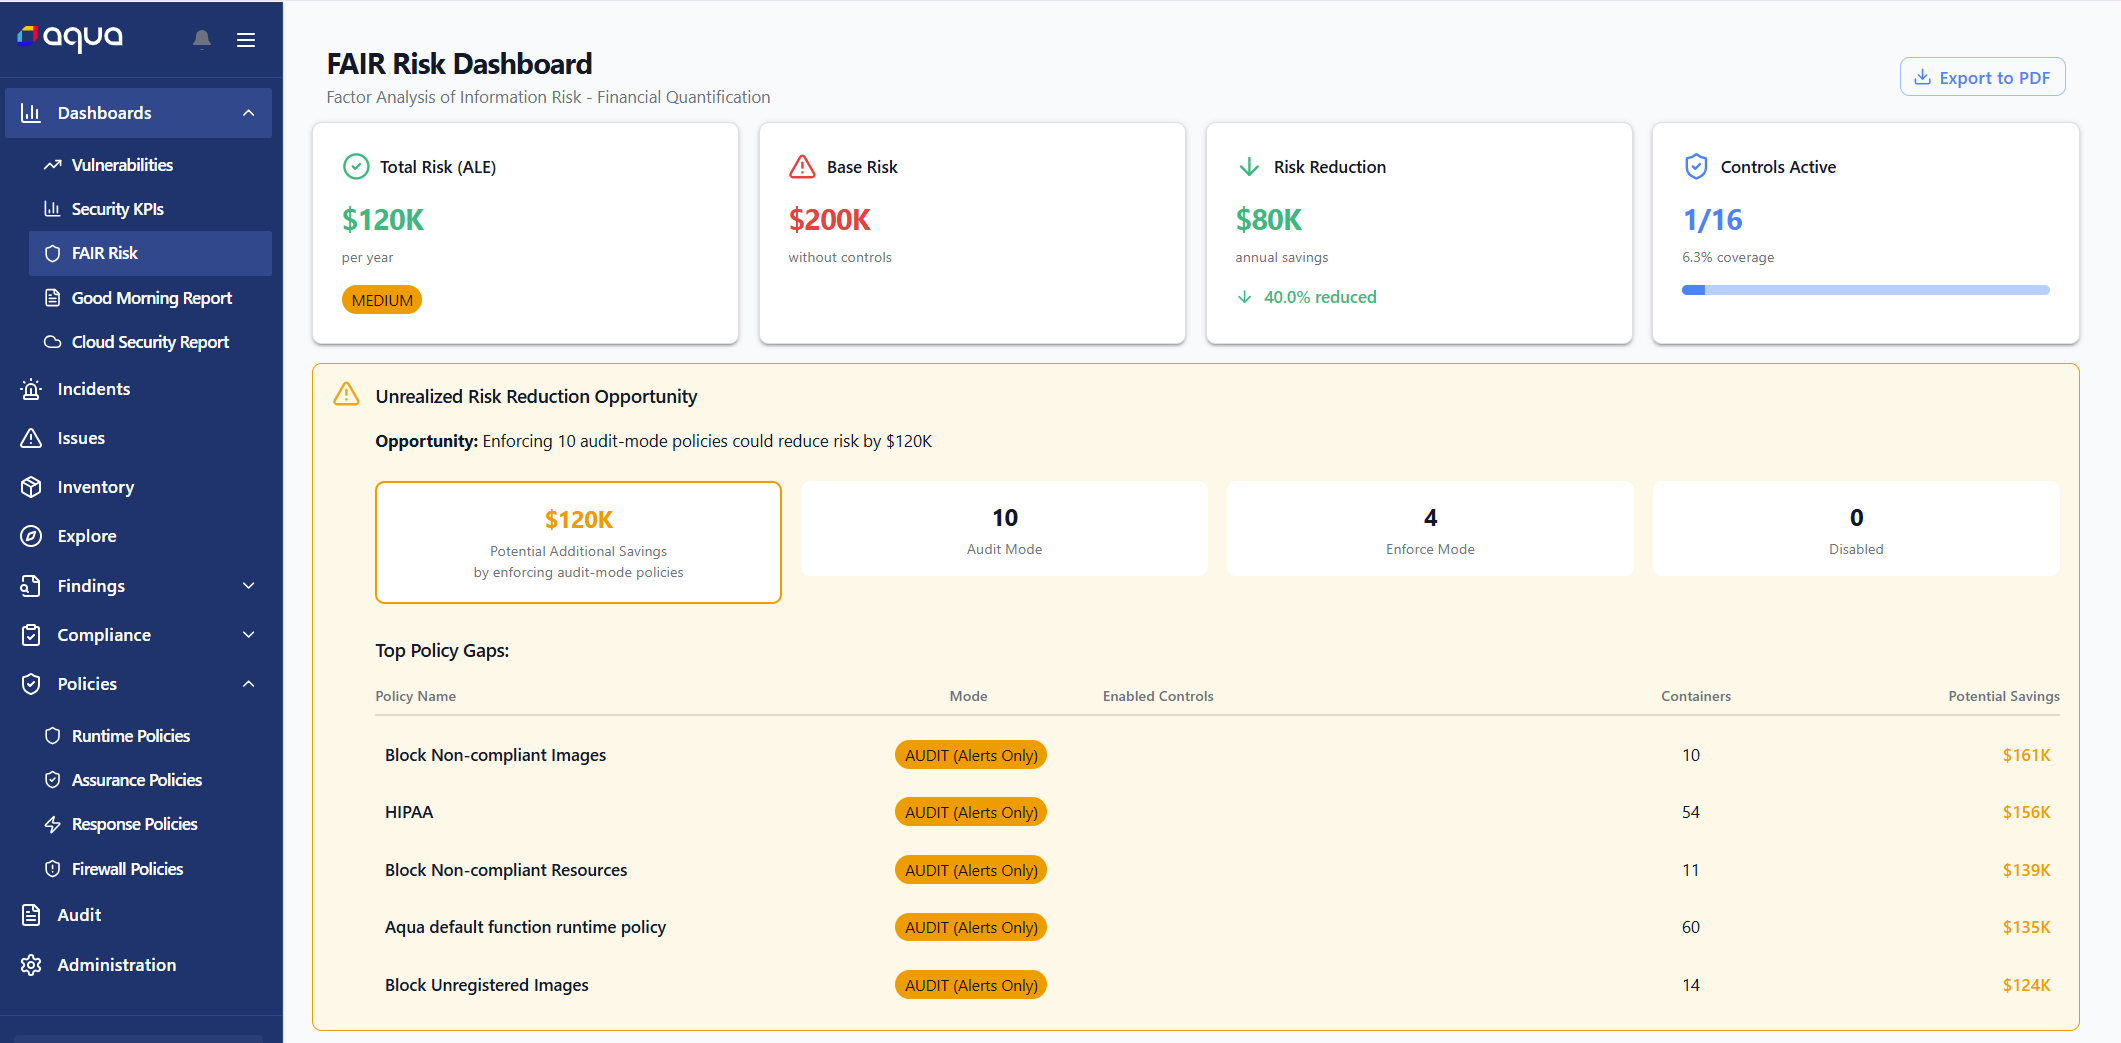
Translate vulnerability, workload and runtime control data into Annual Loss Expectancy to quantify financial exposure and show how enforced controls reduce business risk.
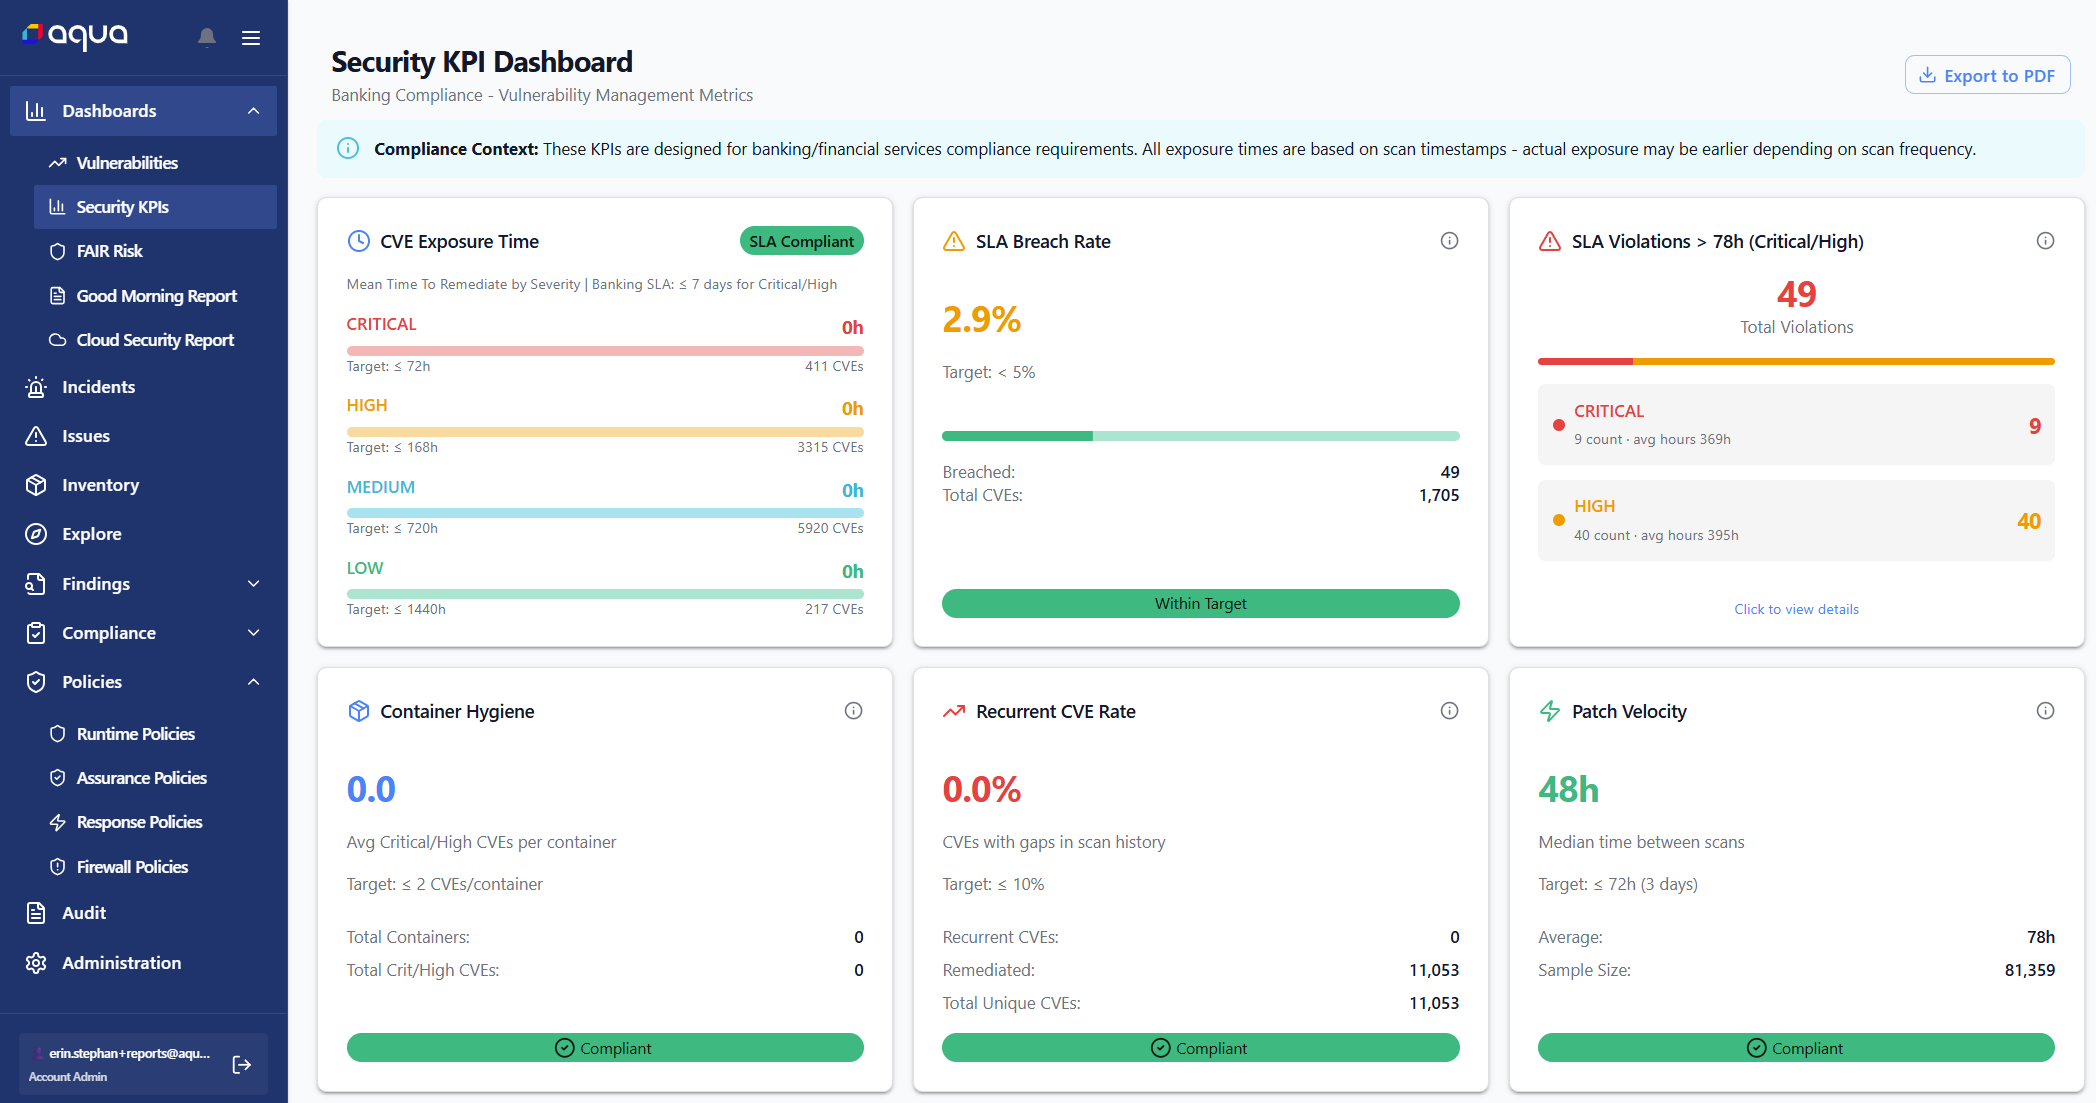
Maintain detailed records of scan results, policy decisions, administrative actions and runtime events so compliance teams can retrieve evidence when assessments begin.
Secure cloud native workloads with a FedRAMP High Authorized platform independently assessed for federal agencies and government partners.


Aqua helps organizations address technical controls and evidence requirements associated with FedRAMP, DORA, NIST, PCI DSS, HIPAA, GDPR, SOC 2 and CIS Benchmarks. Aqua supports an organization’s compliance program but does not make the organization compliant by itself.
Aqua extends Zero Trust principles into cloud native applications by continuously monitoring workload behavior, enforcing approved activity and blocking unauthorized changes and actions at runtime.
Aqua helps organizations implement technical controls associated with NIST guidance through continuous monitoring, vulnerability management, policy enforcement, runtime protection and audit reporting.
Aqua helps financial organizations support DORA initiatives by improving visibility into cloud native workloads, enforcing security controls and maintaining evidence of security events and policy actions. These capabilities support the organization’s broader digital operational resilience program.
Aqua records scan results, configuration findings, policy decisions, administrative actions and runtime events. Teams can use this information to demonstrate how controls were applied and how violations were identified and addressed.
See runtime control stop an attack the moment it tries to execute.