Observe how containers behave before production
Pull in external container images and know exactly how they act before risking the production environment.
Pull in external container images and know exactly how they act before risking the production environment.
Create policies around industry standards like NIST SP 800-218 and enforce container compliance. Verify container images are free of malware, misconfigurations, and vulnerabilities that can compromise the software supply chain.
Mitigate the risks of data theft, credential theft, using containers for DDoS, and cryptocurrency resource abuse targeted by Advanced Persistent Threats and polymorphic malware.
Aqua DTA scans designated images directly from your registries and CI pipelines, preventing malicious images from being deployed in production environments, and “shifting left” incident response.
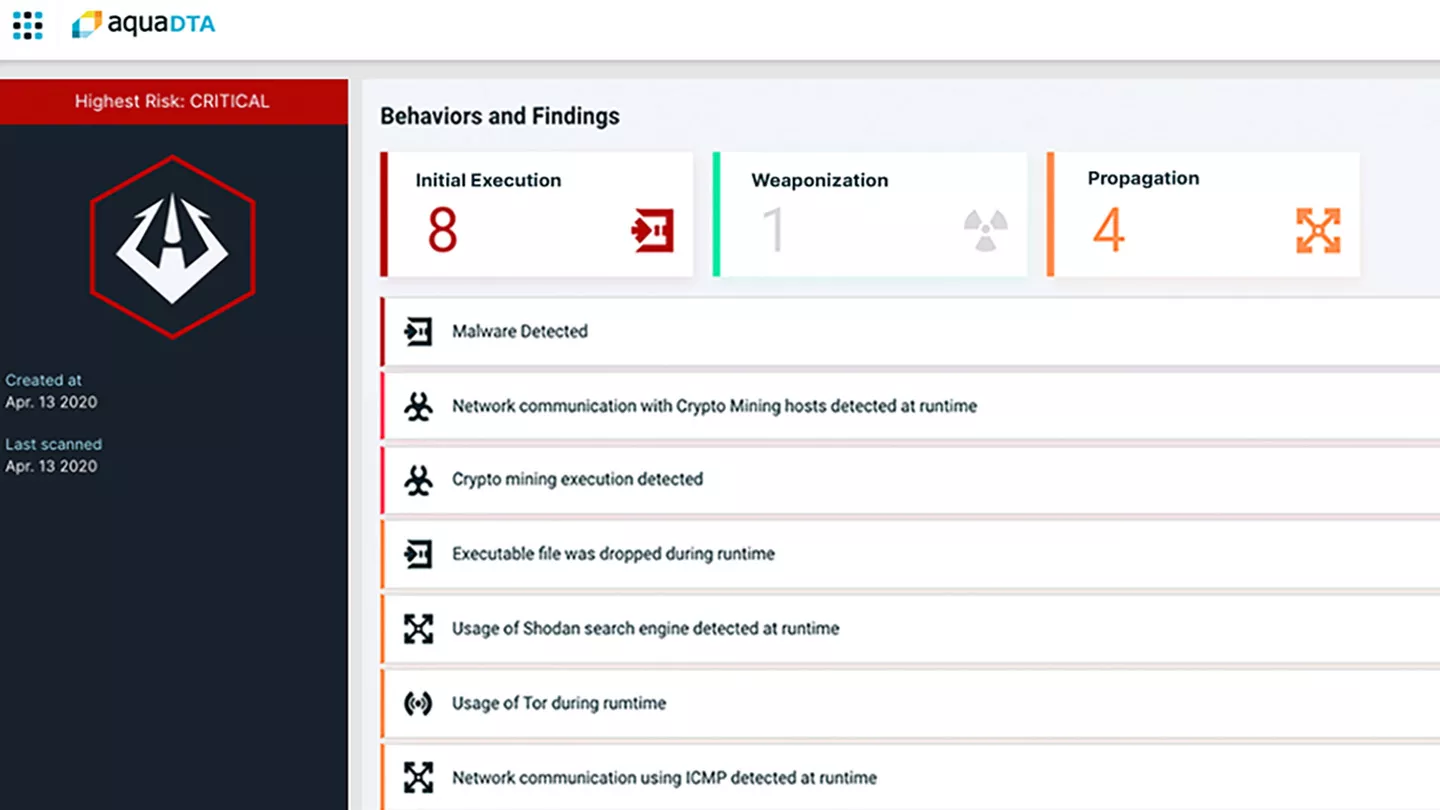
Detects clear indicators of compromise (IoCs) such as container escapes, reverse shell backdoors, malware, cryptocurrency miners, and code injection backdoors, and provides full tracing of all activities.
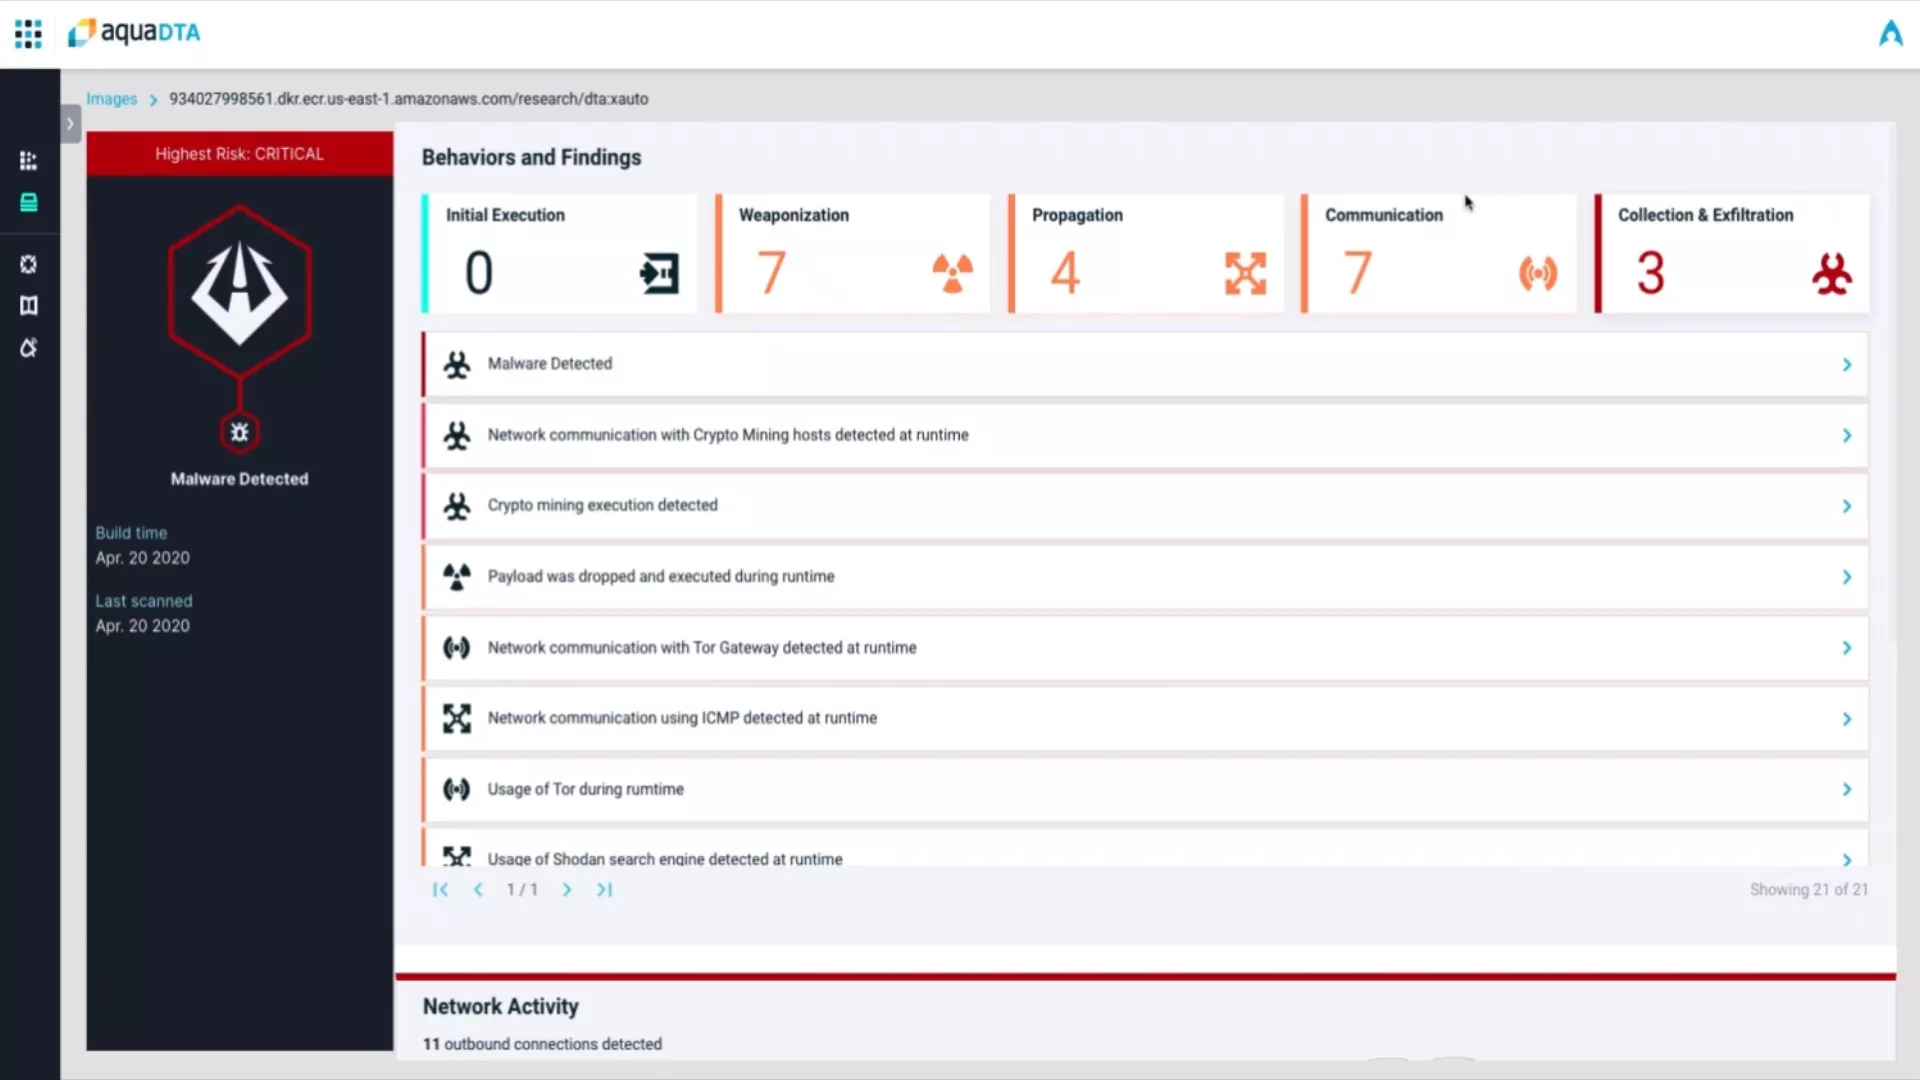
Aqua DTA classifies detected behaviors into categories of the MITRE ATT@CK framework, enabling SecOps and forensics teams to see the entire kill chain and understand and bolster weaknesses in their security infrastructure.
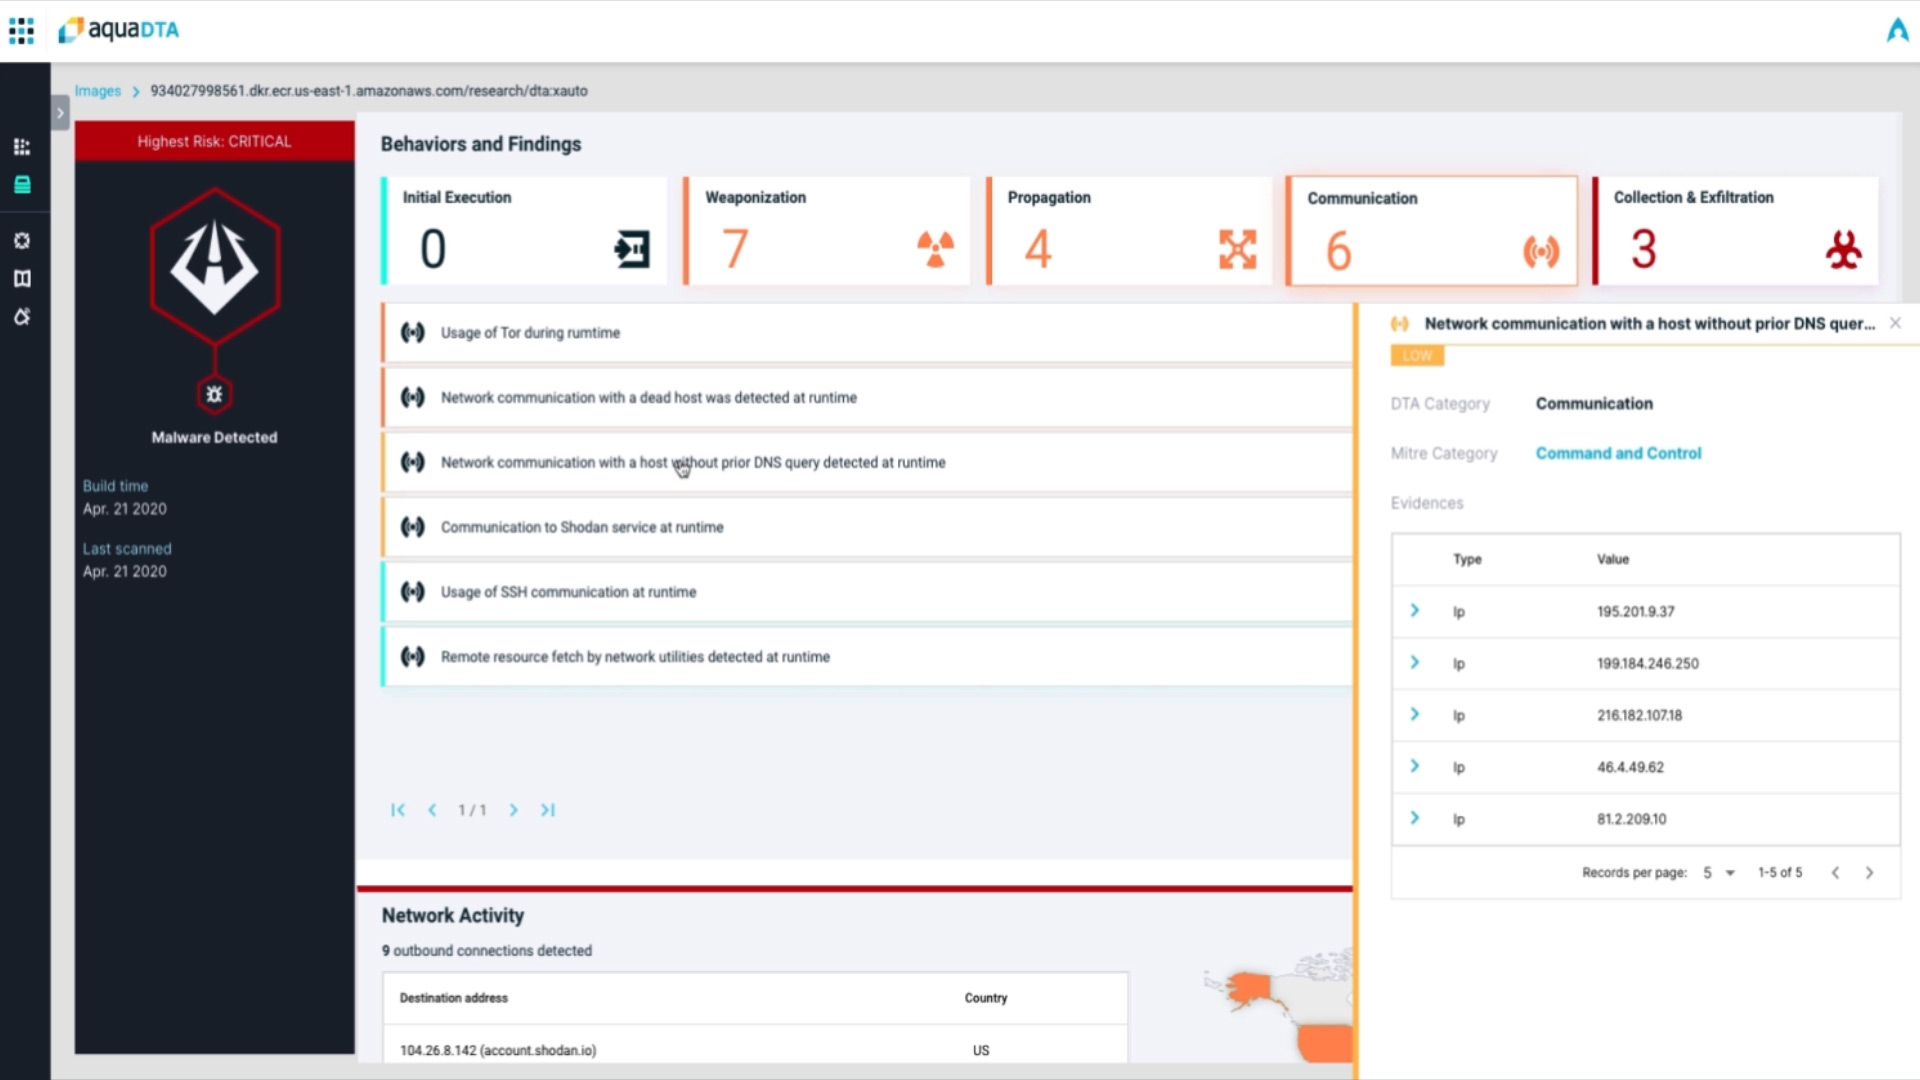
Tracks and displays on a map all communications between the container and external destinations, including file downloads, C&C servers, and data exfiltration destinations.
Go cloud native with the experts!