Solutions · Financial Services

Protect Critical Financial Applications at Runtime

Aquasec delivers runtime security for banks and payment providers, enforcing policies inline, recording audit evidence and translating remaining exposure into financial terms for risk committees and boards.

Map Runtime Evidence to the Industry Frameworks

Assess code, cloud, Kubernetes, image and runtime controls continuously against PCI DSS, SOC 2, NIST and CIS Benchmarks, so evidence reflects how workloads behave today.

Explore Compliance

Express Cloud Risk in Financial Terms

Translate vulnerabilities, threats and applied controls into potential financial exposure with the FAIR Risk Dashboard, and show how that exposure changes as controls take effect.

Explore Vulnerability Management

Enforce Consistent Runtime Policies Across Environments

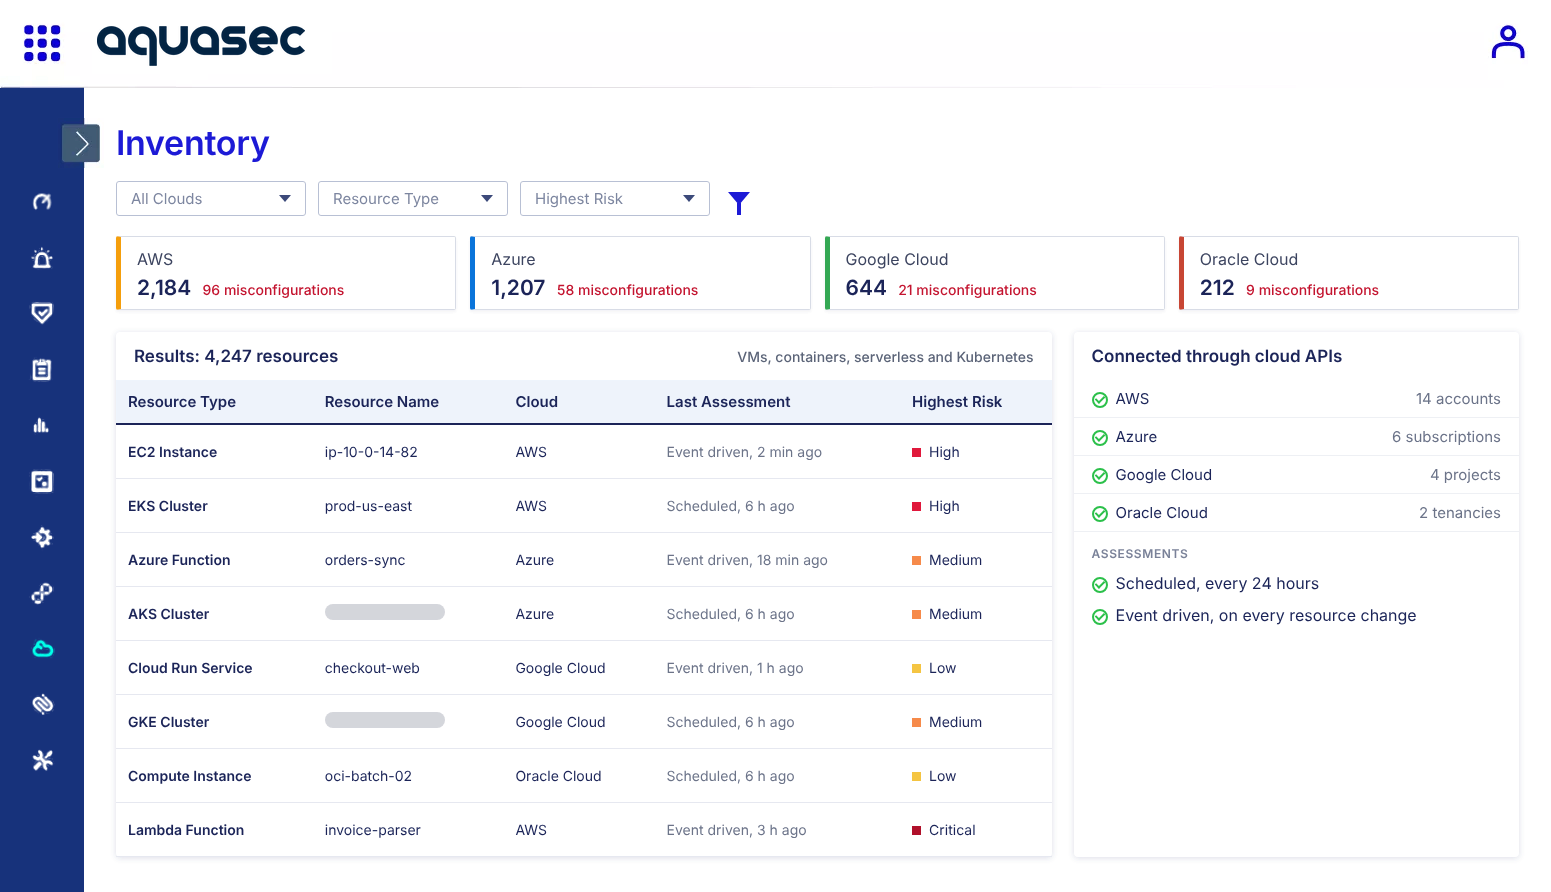
Apply the same runtime policy across public cloud, private cloud and on premises workloads, including environments brought together through an acquisition.

Explore Hybrid Multi Cloud Security
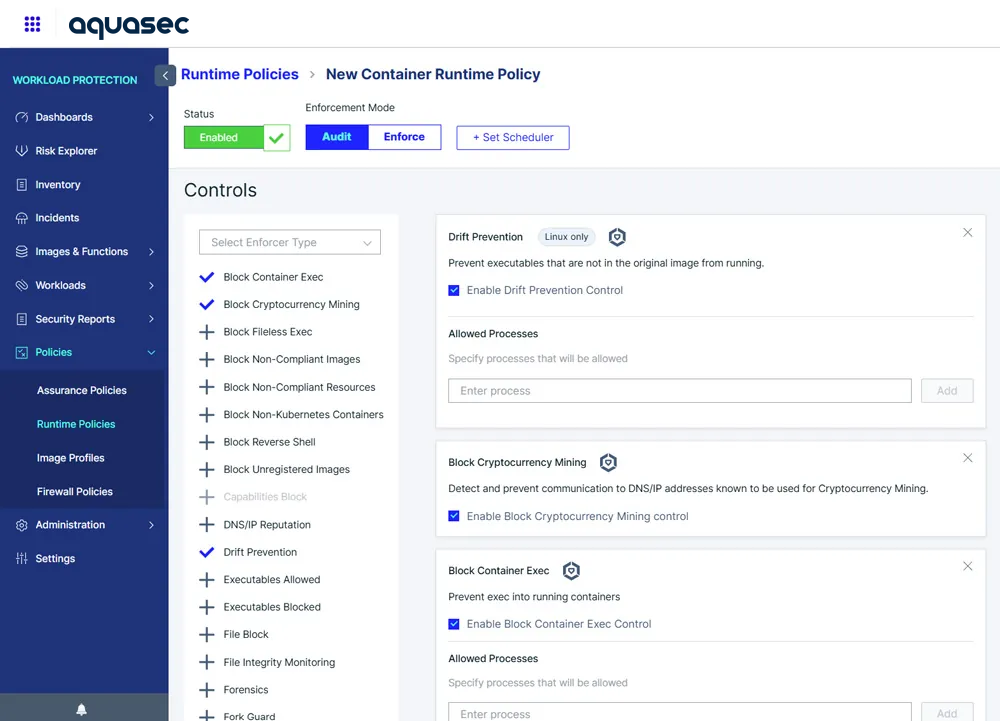
Deny Unauthorized Actions at the Point of Execution

Stop the specific process, file, network or privilege action that violates policy while critical applications keep running. Aquasec Enforcers apply runtime policies such as Drift Prevention at the kernel layer, without making workload termination the default response.
Explore Runtime Security
Deny Unauthorized Actions at the Point of Execution

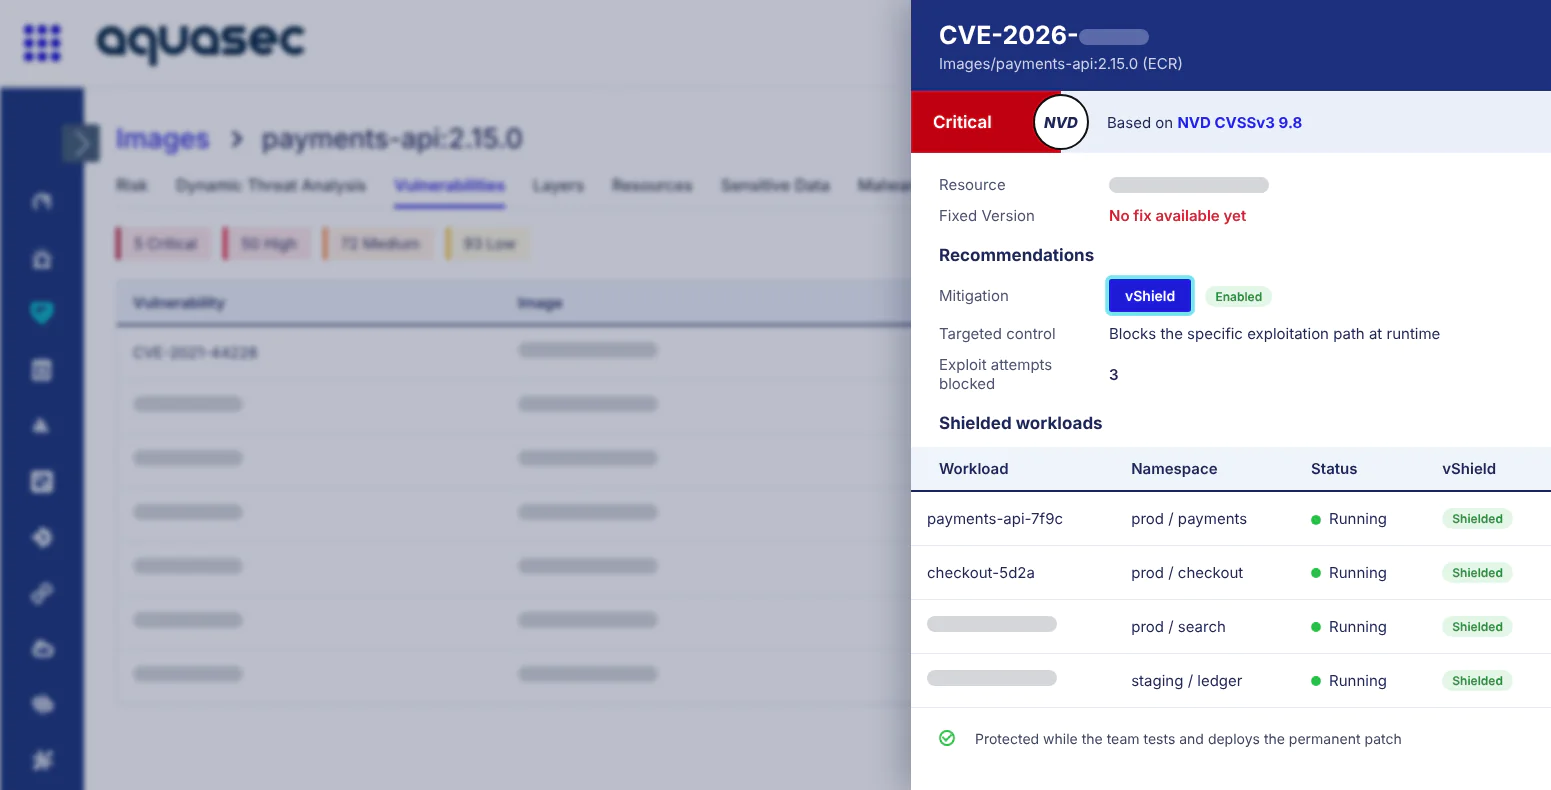
Fix the Vulnerabilities That Expose Production First

Focus remediation on what can affect live applications. Aquasec ranks findings by EPSS, CISA KEV, network exposure and whether the affected workload is running, and vShield applies a compensating control to supported exploitation paths while teams patch.
Explore Vulnerability Management
Fix the Vulnerabilities That Expose Production First

Trace Third Party Software From Production to Its Source

Know which open source components are running and who owns the fix. Aquasec maintains SBOMs and a runtime view of the software present in each workload, then traces each finding to its image, repository, commit and owner.
Explore Code Security
Trace Third Party Software From Production to Its Source

Govern Which AI Models Teams Can Use

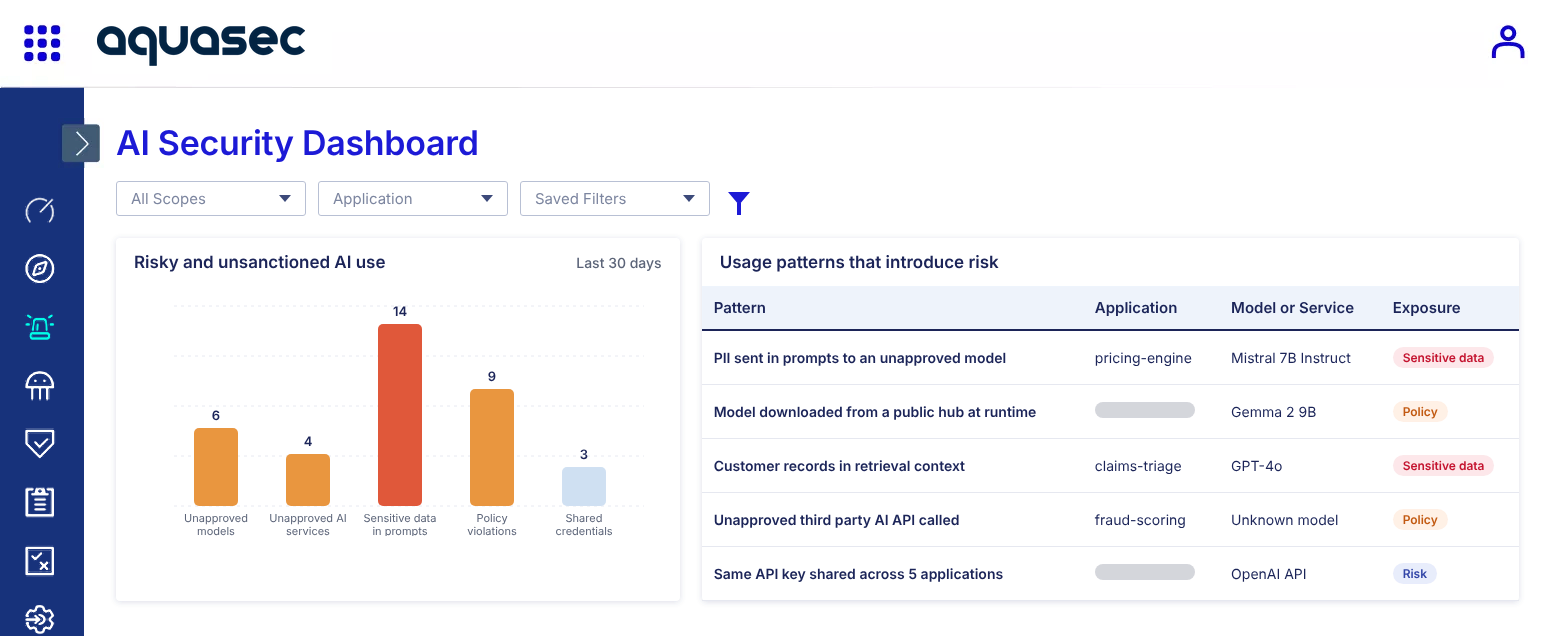
Define the AI services and models your institution has approved and identify unauthorized usage in running applications. Secure AI also inspects supported prompts for injection and sensitive data exposure and protects the workload around the model at runtime.
Explore Secure AI
Govern Which AI Models Teams Can Use
Aqua provides us with full visibility into our Docker environments, with tight controls over privileged user access, automated container security profiles, and real-time enforcement of security policy.
CTO
Fortune 500 Financial Services Company
FAQs
How does Aquasec help financial institutions show that controls are effective?

Aquasec Enforcers apply runtime policy inside each workload and record when each policy was evaluated, enforced or violated. Because that evidence comes from running workloads, auditors see controls operating in production.

Which compliance frameworks does Aquasec support for financial services?

Aquasec continuously assesses code, cloud, Kubernetes, image and runtime controls and maps the evidence to supported frameworks, including PCI DSS, SOC 2, NIST and CIS Benchmarks.

How does Aquasec express cloud risk in financial terms?

The FAIR Risk Dashboard uses FAIR based modeling to estimate potential financial loss from exploitability, likelihood of attack and workload impact. It shows how exposure changes as controls are applied, in terms risk committees and boards already use.

Will runtime enforcement disrupt critical financial applications?

Aquasec denies the specific unauthorized process, file operation, network connection or privilege action rather than making workload termination the default response. Teams can start in audit mode, validate how workloads behave and move each workload group to enforcement once the policy is confirmed.

How does Aquasec govern AI use in financial applications?

Secure AI lets security teams define which AI services and models are approved and flags unauthorized usage in running applications. It also inspects supported prompts for injection and sensitive data exposure, with no application SDK or code changes.

The leading CNAPP for enterprises in the financial sector

Aqua Cloud Native Application Protection Platform (CNAPP)