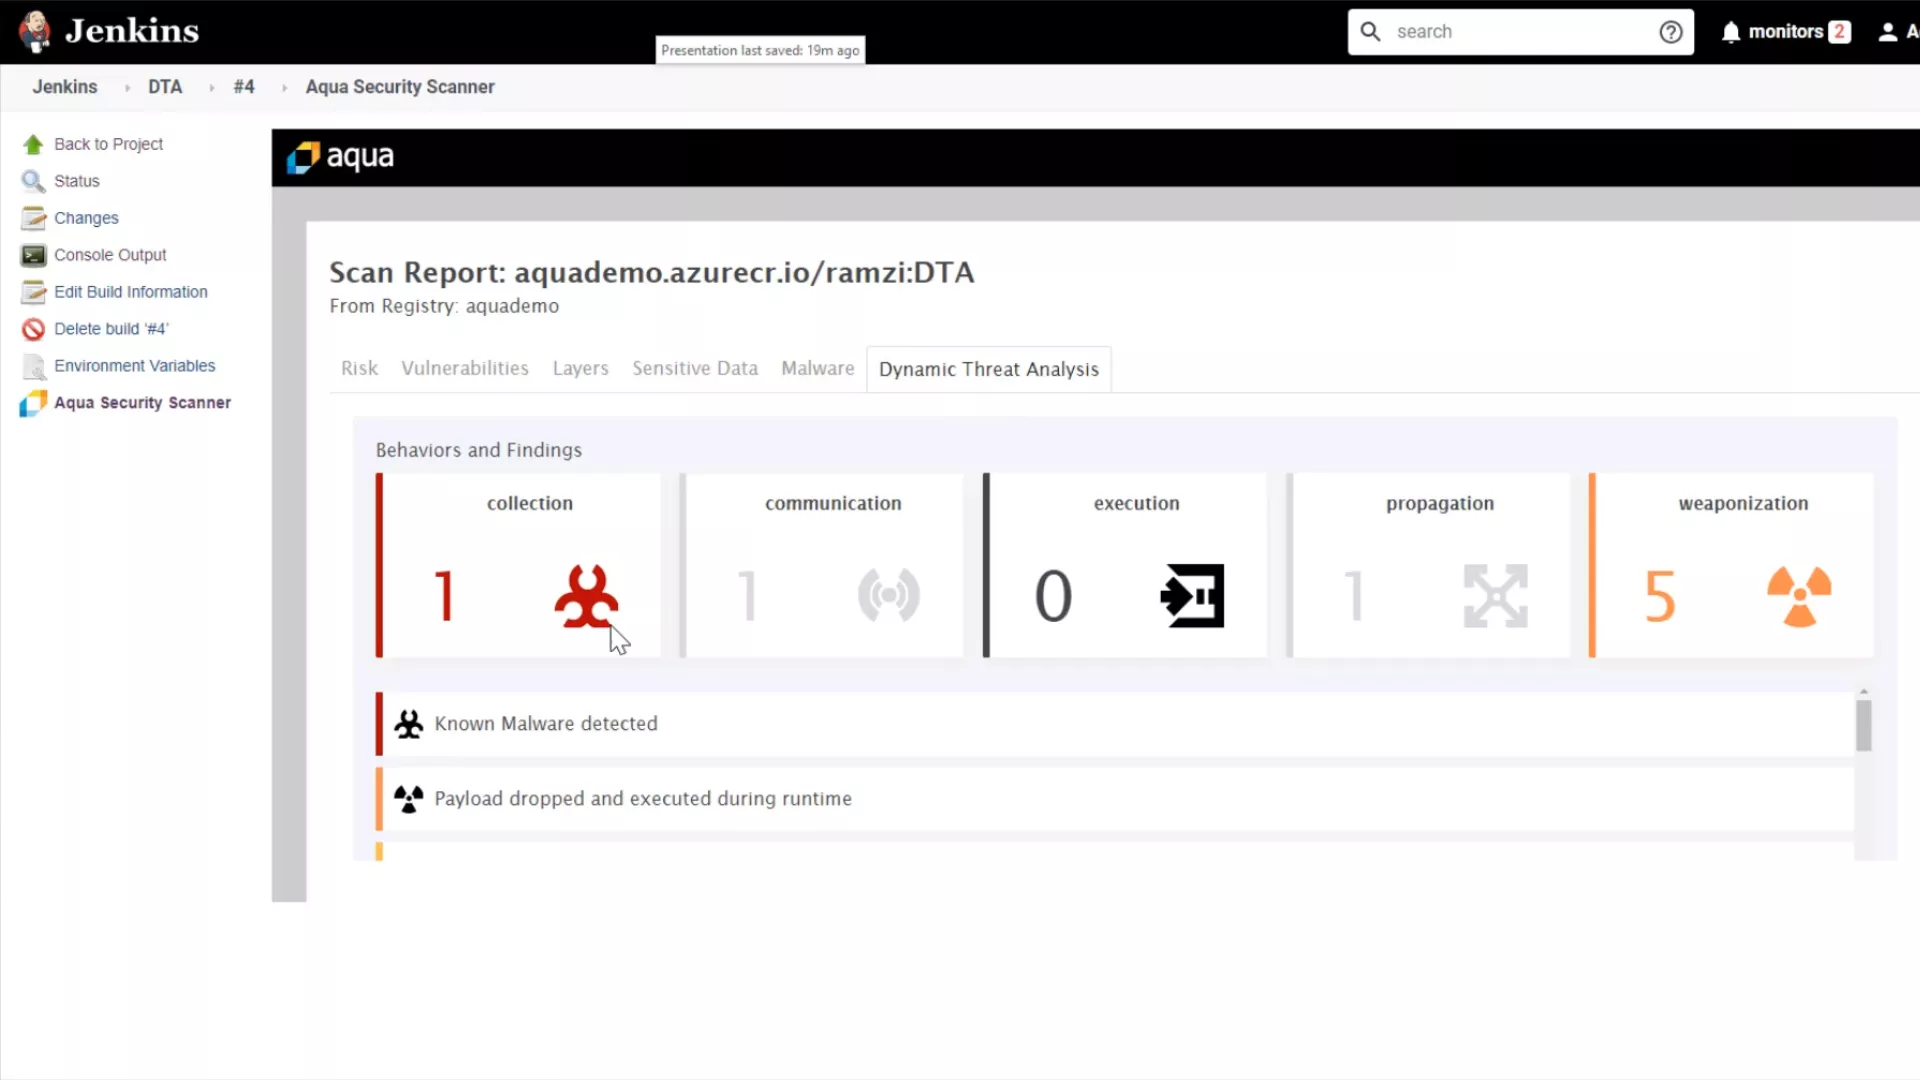
Reliable and accurate detection
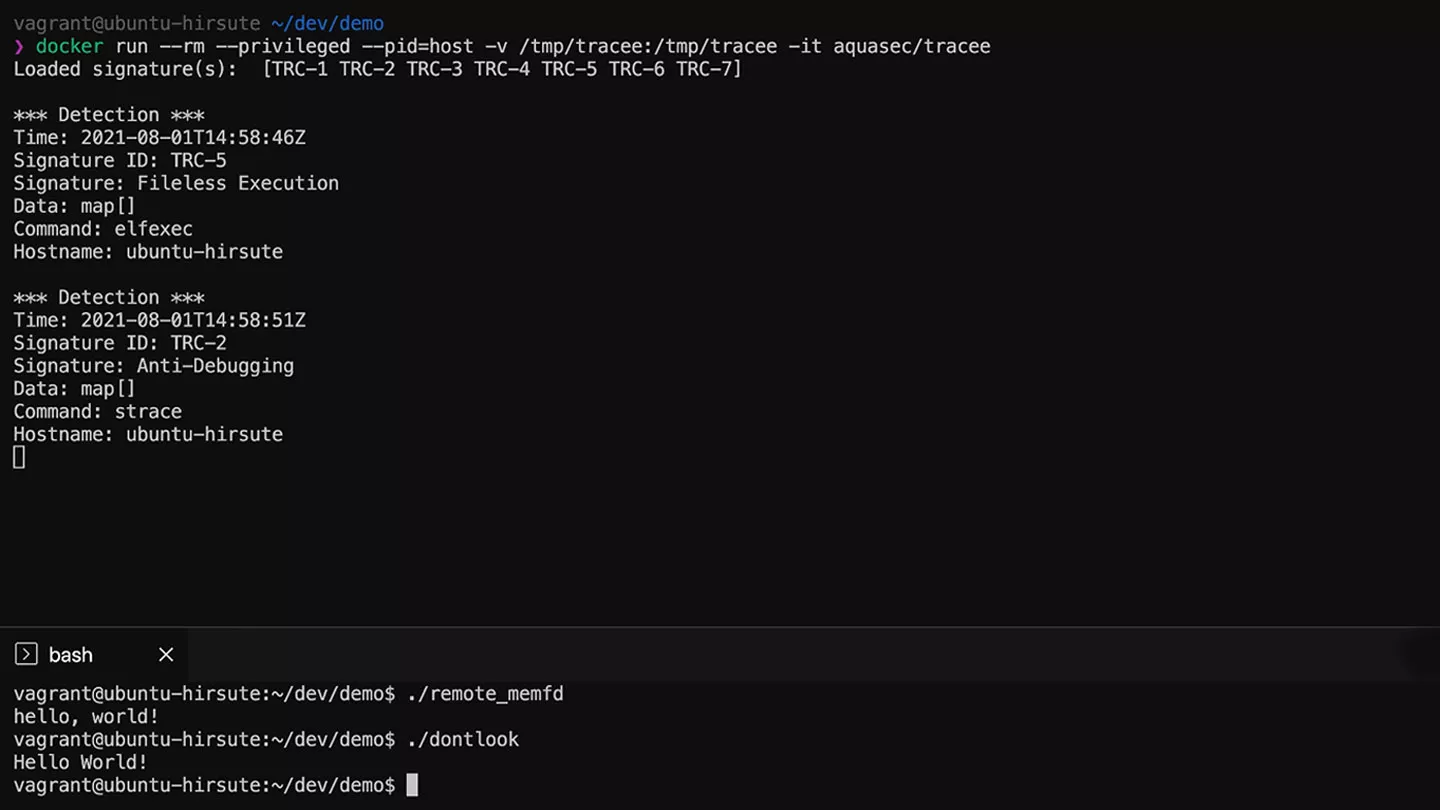
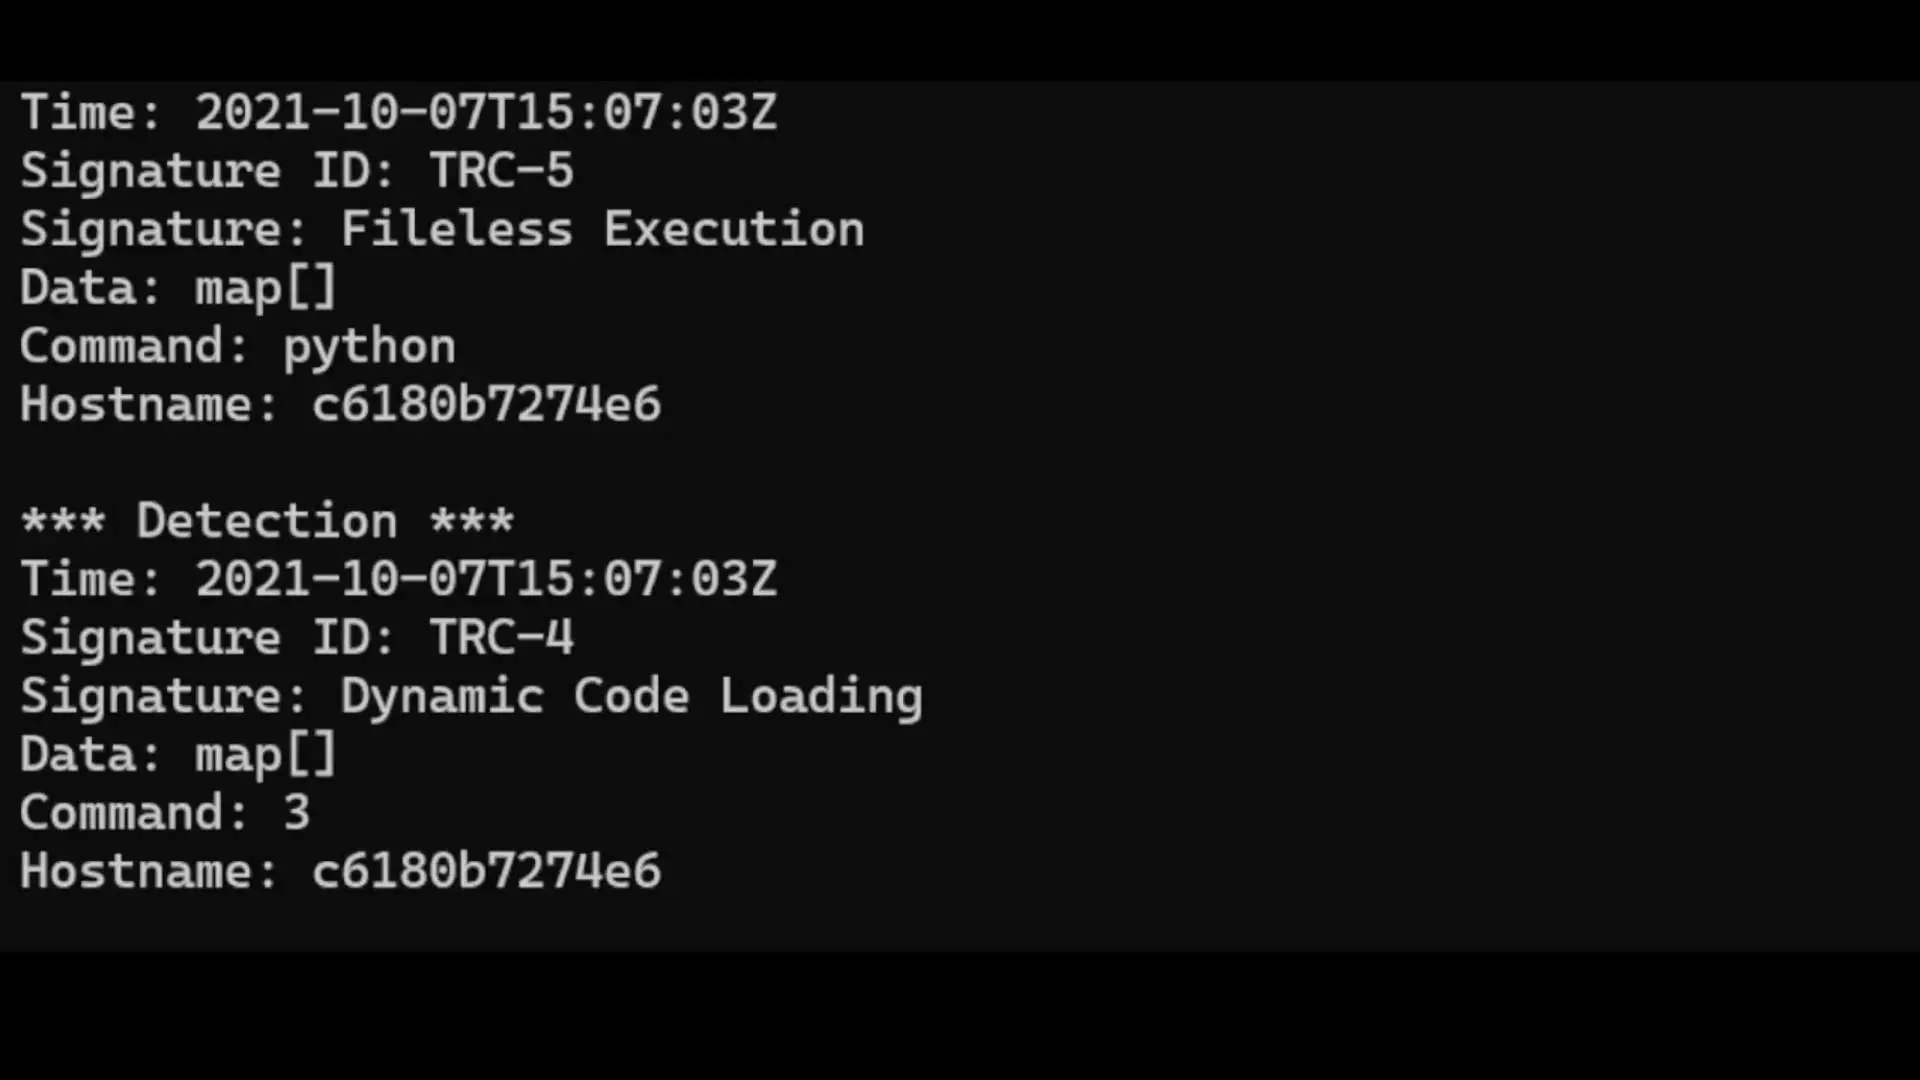
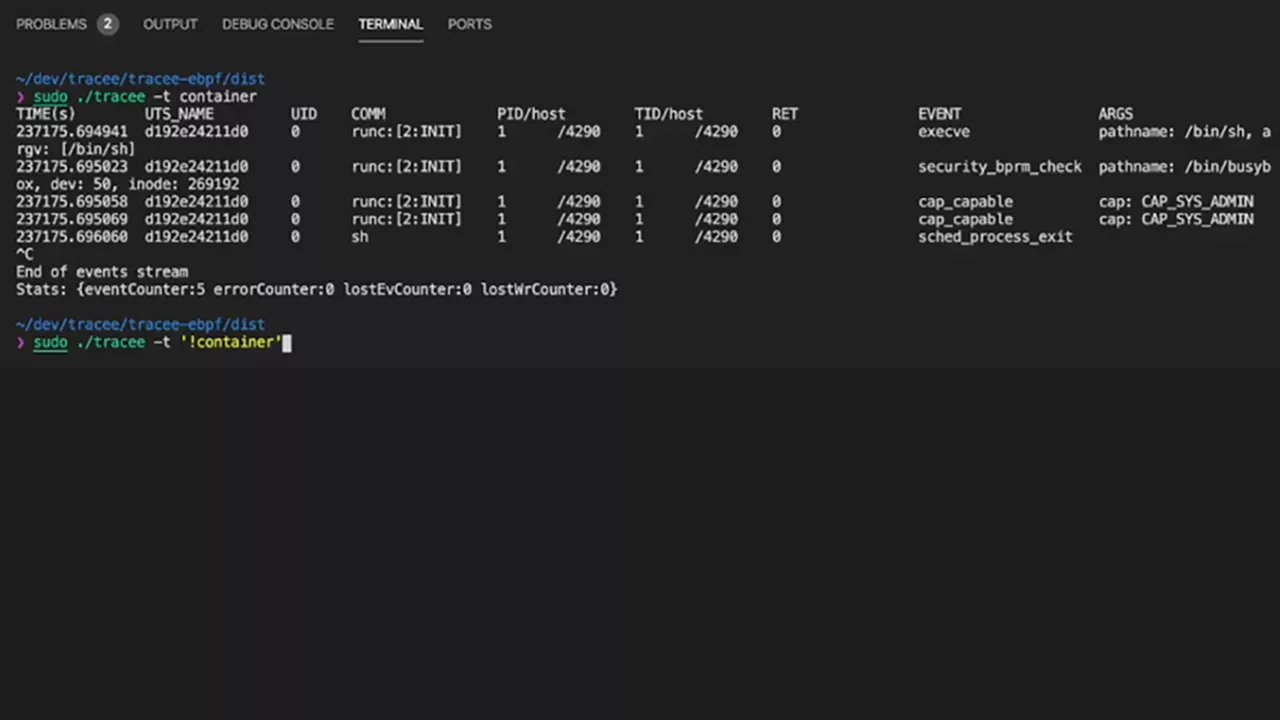
Tracee uses the latest eBPF technology to observe system activity directly from the operating system kernel. With full coverage of Linux system calls, complemented by an additional set of custom security events, Tracee provides high quality, accurate results.
View the Demo