Cloud Shared Responsibility Model: Examples & Best Practices
A shared responsibility model is a framework used in the cloud computing world to define the respective security responsibilities of the customer and the cloud provider.
What Is a Shared Responsibility Model?
A shared responsibility model is a framework used in the cloud computing world to define the respective security responsibilities of the customer and the cloud provider. In this model, the cloud service provider is obligated to secure the underlying infrastructure of the cloud, including physical security, network security, and hypervisor security. The customer, on the other hand, retains the responsibility for securing the data and applications they store and use in the cloud environment, including access control, data encryption, and security configuration.
The shared responsibility security model helps guarantee that cloud security benefits from a collaborative effort between the customer and cloud vendor or provider. By clearly defining each party’s responsibilities, it can help to minimize security risks and ensure that cloud resources are protected against emerging threats and vulnerabilities.
The exact division of responsibilities might differ depending on the type of cloud service being used, such as IaaS (infrastructure as a service), SaaS (software as a service), or PaaS (platform as a service). The following diagram from the Center of Internet Security (CIS) illustrates the differences in division of responsibility across different cloud models.
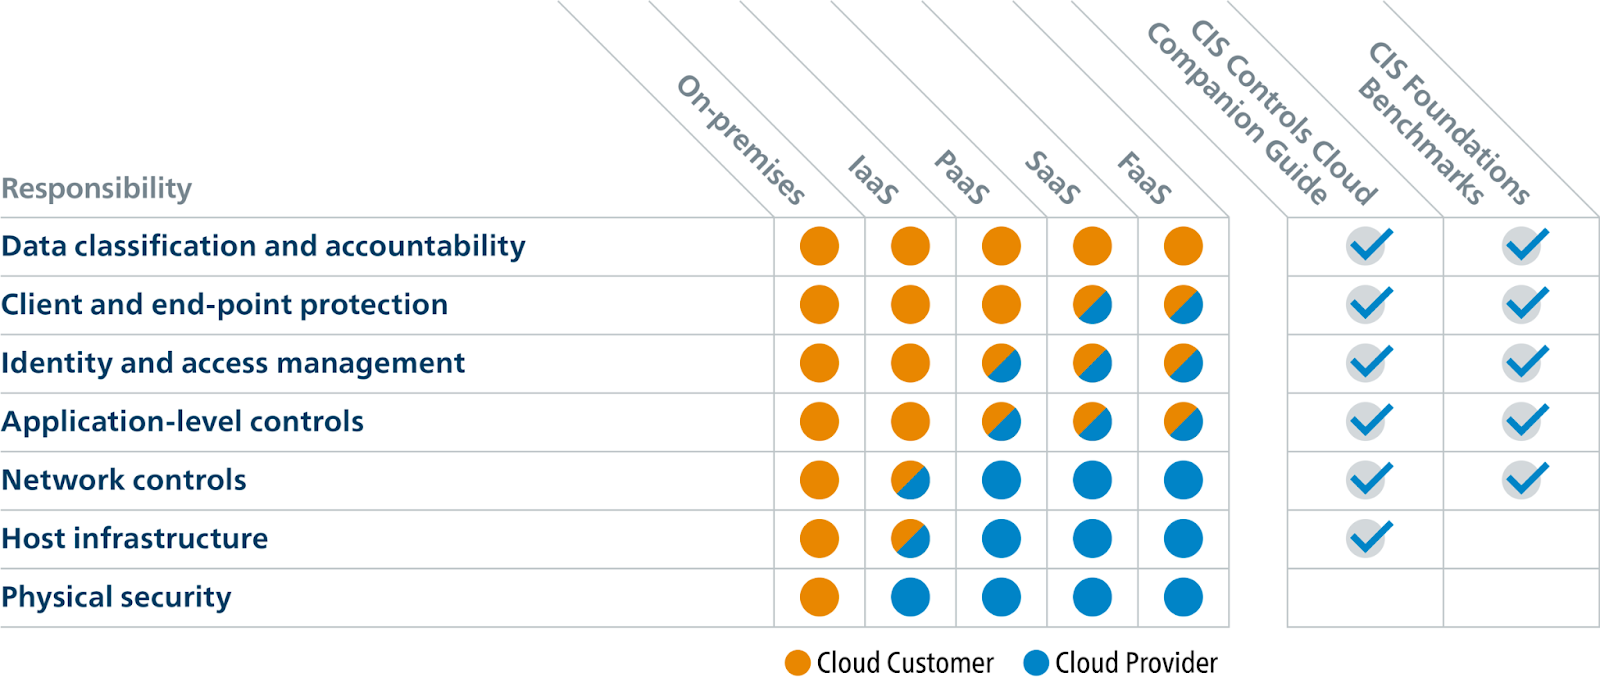
Source: Center for Internet Security
This is part of a series of articles about cloud security.
In this article:
Examples of Shared Responsibility Models
Here are some examples of the shared responsibility models for popular cloud providers.
AWS
The shared responsibility model for Amazon Web Services (AWS) defines the security responsibilities of AWS and its customers. In this model, AWS is accountable for securing the cloud infrastructure’s underlying components, including the physical data center security, network security, and hardware security. On the other hand, AWS customers must secure their data and applications stored and used on AWS by controlling access, implementing data encryption, and configuring security settings.
For AWS compute and storage services such as the Elastic Compute Cloud (EC2) and the Elastic Block Store (EBS), the customer has a high degree of control over the services. Thus, the customer also assumes a significant share of the responsibility for the service’s security. Amazon focuses on protecting the physical networking and servers, as well as virtualization technologies, that support the cloud.
Azure
The shared responsibility security model in Azure defines the security responsibilities of Microsoft Azure and its customers. Under Azure’s shared responsibility cloud model, Microsoft is responsible for the security of the physical infrastructure of its data centers, as well as the virtualization layers, such as the hardware, hypervisor, and networking components. Azure also carries responsibility for the security of the Azure services themselves, such as Azure Kubernetes Service (AKS), Cosmos DB, container instances, data lake storage, and blob storage.
In the case of Infrastructure as a Service (IaaS), customers must secure the virtual machines, storage, and network security groups that they provision on Azure. For PaaS and SaaS services, the responsibility for securing the underlying infrastructure is primarily with Azure, while the customer retains responsibility for securing the applications and data.
To help customers understand and fulfill their security responsibilities, Azure provides a variety of security tools and services, such as Azure Security Center, Azure Active Directory, and Azure Key Vault. Azure also provides detailed documentation and best practices to help customers implement effective security controls in their Azure environment.
Google Cloud
The Google Cloud Platform (GCP) shared responsibility model defines the responsibilities of both Google and the customer in securing the customer’s data and applications on the GCP platform.
Under this security model, Google is responsible for protecting the infrastructure that runs GCP, including physical data center security, network security, and the security of the underlying virtualization technology. Google also provides various security services and features, such as encryption of data at rest and in transit, and access controls, to help customers secure their data and applications.
The customer is responsible for securing their own data and applications, including securing the configuration and management of their virtual machines, storage, and networks. The customer must also ensure that their own applications and data are secure, including implementing appropriate access controls and data protection measures.
5 Best Practices for Handling Shared Responsibility
When managing the shared responsibility for cloud security, following best practices can helps organizations ensure that their cloud resources are secure:
- Review each cloud provider’s SLAs: The first step when choosing a cloud service provider (CSP) is to review the service level agreements (SLAs) carefully. This includes understanding all the security features and protections offered and verifying that they meet the organization’s specific security requirements. Seemingly minor differences between SLAs can have significant implications for security and liability. Another important consideration is to ensure that the provider’s SLAs include clear service uptime and data recovery objectives.
- Focus on securing data: The main priority for a cloud customer is to secure data stored in the cloud. This aspect of security is primarily the customer’s responsibility. Data security includes encrypting sensitive data at rest and in transit, using secure protocols for accessing cloud resources, and carefully managing data access and permissions. Customers must ensure that they have data protection policies and procedures to protect sensitive data against unauthorized access, loss, or theft.
- Implement identity and access management (IAM): Another aspect of the customer’s security burden is access control, which is best achieved using an effective IAM system. This involves managing user access, roles, and permissions, as well as implementing multi-factor authentication (MFA) and other identity verification mechanisms. IAM policies and procedures should be implemented to ensure that only authorized personnel can access sensitive data or applications.
- Address misconfigurations: Misconfigurations can lead to vulnerabilities and potential security breaches, and are primarily within the responsibility of the cloud customer. It’s essential for organizations to identify, remediate, and prevent misconfigurations—this involves implementing secure configurations and regularly auditing infrastructure and application settings. Automated tools can help monitor for misconfigurations in real-time, allowing organizations to detect and address potential risks.
- Choose a trusted cloud security partner: Cloud security partners can provide a range of services, including security assessments, threat monitoring, incident response, and security consulting. When selecting a cloud security partner, it is important to choose a partner that has a proven track record of success, strong industry certifications, and experience in managing cloud security risks. A cybersecurity specialist can help organizations choose the right cloud provider and service model, ensuring they have the tools and knowledge they need to enforce their security responsibilities.
Why You Need Security Beyond Cloud Provider Offerings
Cloud Security Posture Management (CSPM) is a critical component of cloud security, as it helps organizations to maintain and manage the security posture of all cloud-based resources.
While cloud providers, such as Amazon Web Services (AWS), Microsoft Azure, and Google Cloud Platform (GCP), offer a range of security features and services, there are a number of reasons why organizations may need additional CSPM measures beyond what the cloud provider offers:
- Multi-cloud: Most organizations today use multiple cloud platforms, and security options provided by cloud providers are typically compatible only with their own cloud services. Third party cloud security solutions can provide unified security across clouds.
- Complexity: Cloud environments are complex and dynamic, and organizations may need additional tools and processes to manage and maintain the security posture of their cloud-based resources. In addition, some cloud provider security solutions are complex to deploy and operate, because they are based on existing, repurposed tools.
- Customization: The security features and services provided by cloud providers are typically limited to cloud configurations. However, organizations have additional security needs that go beyond cloud configurations—for example, an organization may need to implement additional security controls, such as firewalls or intrusion detection systems (IDS).
- Threats: Cloud environments are still vulnerable to threats, such as malware, data breaches, and cyberattacks. Organizations may need to implement additional security measures, such as threat intelligence and incident response, to detect and respond to threats. Without dedicated cloud native security solutions, organizations may not have the data and technological capacity to detect and prevent cloud-based attacks.
By implementing additional CSPM measures beyond what the cloud provider offers, organizations can better manage and maintain the security posture of their cloud-based resources, meet their specific security needs and requirements, and ensure compliance with regulations and standards. It’s important to understand that while cloud providers offer a range of security features and services, organizations must still take an active role in securing their cloud-based resources.
Aqua Cloud Native Application Protection Platform (CNAPP)
Go cloud native with the experts!