8 Critical Azure Security Best Practices
Discover critical best practices that can help you secure your Azure cloud deployment, and understand the Azure shared responsibility security model.
Azure uses a shared responsibility model, where Microsoft as the cloud provider is responsible for securing the infrastructure, and your organization as the cloud customers is responsible for securing workloads and data. You are also responsible for configuring Azure security options.
We’ll explain the shared responsibility model in cloud security and show how to define eight essential security options to secure your Azure cloud.
In this article:
- Azure Shared Responsibility Model
- Leveraging-Azure-Security-Services
- Azure-Active-Directory-(Azure-AD)
- Azure Security Center
- Network Security Groups (NSGs)
- Azure Security Best Practices for Specific Services
- Azure App Service
- Azure Kubernetes Service (AKS)
- Azure Storage Accounts
- Azure Blob Storage
- Azure Tables
- Cloud Security Posture Management (CSPM) in Azure with Aqua Security
Azure Shared Responsibility Model
Microsoft Azure has a shared responsibility security model. Microsoft and your organization, as the cloud user, share responsibility for aspects of Azure security. Security lapses can happen if you don’t fully understand the division of responsibility and the security tools and services Azure provides.
Depending on the Azure services you use, you assume more or less responsibility for security. The following table illustrates who is responsible for security in different aspects of an Azure cloud deployment.
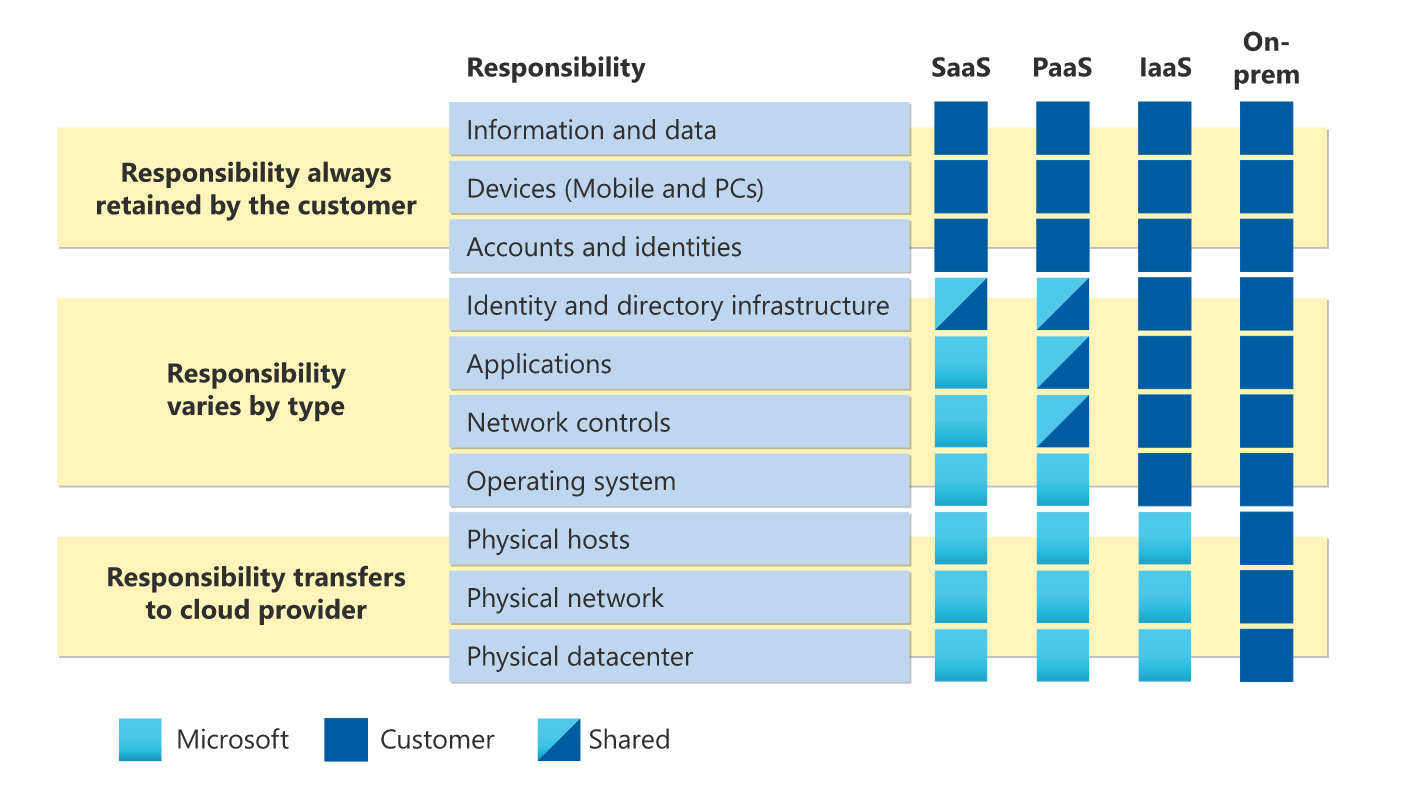
Image Source: Microsoft
Infrastructure as a Service (IaaS) is a cloud computing service model in which the cloud provider handles the underlying compute, storage, and networking infrastructure. For IaaS services like Azure virtual machines (VMs):
- Microsoft’s responsibilities include securing physical machines, network hardware, and the hypervisor.
- User’s responsibilities include securing the operating system, network configuration, identity management, data storage, and applications.
For Platform as a Service (PaaS) services like Azure SQL Database:
- Microsoft’s responsibilities include all of the above, and in addition, securing network configuration and the operating system
- User’s responsibilities are limited to information and data, end-user devices, accounts and identities. Users also have responsibility for securely configuring identity management, applications, and network controls.
For Software as a Service (SaaS) services like Office 365:
- Microsoft’s responsibilities include all of the above, and in addition, securing identity infrastructure, networks, and applications.
- User’s responsibilities are limited to information and data, end-user devices, accounts and identities, as well as securely configuring identity infrastructure.
Related content: Read our guide to Azure cloud security
Leveraging Azure Security Services
1. Azure Active Directory (Azure AD)
Azure AD is an enterprise identity management service, which can help you set up user accounts and permissions for all Azure services. It also integrates with on-premise Active Directory deployments to enable hybrid access.
Leveraging Azure AD for enhanced security:
- Select the option Admin Enabled—this allows users to manage account administrators in a centralized manner within Azure AD. It enforces key rotation andstrong permission management across all servers and databases in Azure.
2. Azure Security Center
Azure Security Center provides security management and threat protection for all cloud services you run in the Azure cloud. It can discover unsecured cloud resources and threats in your environment and provide recommendations for remediation.
Leveraging Azure Security Center to enhance your Azure security posture:
- Enable Admin Security Alerts—this enables Security Center to send alerts to the admin of the relevant Azure subscription, providing visibility over security issues and allowing admins to take action.
- Enable Security Configuration Monitoring—this option turns on monitoring and ensures that Azure Security Monitor continuously collects data about virtual machines running in your Azure environment.
3. Network Security Groups (NSGs)
NSGs are an important part of Azure security. They filter network traffic between resources in Azure virtual networks (VNets). Almost all Azure services, including VMs, Azure Containers and Azure Functions, can be deployed into a VNet to enhance security. An NSG contains security rules that define which traffic is allowed or denied for each resource in Azure.
Leverage NSGs to enhance security:
- Define a Default Security Group and set it to block all traffic by default—this makes sure that any security group created without specific settings denies all traffic. This prevents accidental exposure of Azure resources.
Azure Security Best Practices for Specific Services
Here are key best practices that will help you securely configure Azure services.
Related content: Read our guide to cloud workload security
4. Azure App Service
Azure App Service is a managed platform for running web applications and APIs. It supports applications written in many popular languages including Java, .NET, PHP, Node.js, and Python, and can run Windows or Linux contains.
Securing Azure App Service:
- Select the option Identity Enabled—this ensures that authenticating with applications can only be performed by managed identities, not by credentials stored in the code. Secrets stored in plaintext as part of your application code represent a major security risk. You can set up managed identities via the integration between App Service and Azure Active Directory (AD), which also enables role-based access control (RBAC).
5. Azure Kubernetes Service (AKS)
AKS is a managed Kubernetes service that lets you deploy containerized applications without having to install and manage the Kubernetes control plane.
Securing AKS:
- Enable Kubernetes RBAC—when using RBAC in AKS, it can be tied to Azure AD roles. By turning on RBAC, you ensure only authorized users can access AKS and clusters running on it.
- Deploy the latest version of Kubernetes—AKS can provision clusters using several versions of Kubernetes. Always use the latest version, to ensure you benefit from the most recent patches and security updates.
6. Azure Storage Accounts
An Azure Storage account defines your Azure storage options, including blob storage, file storage, and table storage.
Securing Azure storage accounts:
- Disable Log container public access—this means the activity log container is not accessible to the public, preventing exposure of activity logs, which might be valuable to attackers.
7. Azure Blob Storage
Azure Blob Storage is an elastically scalable object storage service. It supports Azure AD roles, allowing you to use the same user permissions across all Azure services that require access to blob storage.
Securing Azure Blob Storage:
- Enable Blob Container Private Access —this ensures that blob containers always require authentication. A blob container with public access can be viewed by anonymous users, which presents a security risk.
8. Azure Tables
Azure Tables is a schemaless NoSQL data store.
Securing Azure Tables:
- Enable Table Service All Access—this option uses the Azure Table Service Access Control List (ACL). Configure ACLs according to the least privilege principle—users should only have access to view or perform actions on a table if they must have access to perform their roles.
Cloud Security Posture Management (CSPM) in Azure with Aqua Security
As we have noted, security in the cloud is a shared responsibility between the customer and the cloud provider like AWS, Azure, or Google. The model requires users be responsible for securing their applications and infrastructure configurations and settings running in the cloud, while the cloud provider ensures the security of the cloud itself.
Cloud providers are responsible for securing the underlying infrastructure – including the hardware, software, networking, and facilities – with customer responsibility determined by the AWS Cloud services that a customer selects.
This means that cloud users are the ones responsible for properly configuring their own guest operating systems, databases, and applications. They should take care of such areas as network traffic security, OS and firewall configuration, application security, patching, identity, and access management, and, most critically, the safety of customer data..
The Aqua Enterprise platform provides comprehensive security for the entire lifecycle and configuration of container-based and cloud-native applications, with consistent policies and controls, from image build to deployment for a broad set of cloud-native Microsoft Azure build, infrastructure, deployment and runtime services.
Aqua Cloud Native Application Protection Platform (CNAPP)
Go cloud native with the experts!