- Cloud Native Applications
- Application Security
- Web Application Security
- Application Security Posture Management (ASPM)
- Microsegmentation
- Python Security
- SaaS Security
- Node.JS Security
- PHP Security
- AI in Cyber Security
- Cybersecurity for Financial Services
- The Principle of Least Privilege (PoLP)
- Identity and Access Management
- Cybersecurity in Banking
- Threat Detection and Response
- Cyber Kill Chain
- Threat Hunting
- Zero Trust Security
- Zero Trust Architecture
- Fileless Attacks
- DSPM
- Container Scanning
- Kubernetes
- Kubernetes
- Kubernetes Alternatives
- Kubernetes Namespace
- Kubernetes Architecture
- Kubernetes Cluster
- Kubernetes Nodes
- Kubernetes Pods
- Kubernetes Jobs
- Kubernetes Workloads
- Kubernetes Monitoring
- Kubernetes Security
- Kubernetes RBAC
- Secret Scanning
- Kubernetes Security Posture Management (KSPM)
- Kubernetes on AWS
- Kubernetes on VMware
- Kubernetes Vulnerability Scanning
- Managing Containers in Kubernetes
- K3s
- eBPF in Kubernetes
- Kubernetes Dashboard
- Kubernetes Operators
- Kubernetes Services
- Kubernetes Devops
- Kubernetes Networking
- Kubernetes ConfigMap
- Kubernetes Management
- Kubernetes Helm
- Kubernetes as a Service
- Kubernetes Serverless
- Kubernetes Tutorials
- Cloud Attacks
- Cloud Attacks
- Malware Attacks
- Zero Day Attack
- Top 10 Cyber Security Threats
- Arbitrary Code Execution
- Cryptojacking
- AI Attacks
- Prompt Injection
- Backdoor Attacks
- Reverse Shell Attack
- Remote Code Execution
- Defense Evasion
- Honeypots in Cybersecurity
- Malware Analysis
- AI Malware
- Lateral Movement
- Advanced Malware Protection
- CNAPP
- AI Security
- Container Platforms
- Containerized Architecture
- Docker Secrets
- Container Runtime Interface
- Container Images
- Image Scanning
- Container Compliance
- Docker Security Best Practices
- Container Security
- Container Security Best Practices
- Container Security Tools
- ECS Security
- Network Segmentation
- Istio security
- runC
- Service Mesh
- Image Repository
- Container Escape
- Container Runtime
- Docker Container
- OSS Container Image Scanning Tools
- What Is a Container?
- Docker Images
- Containerization 101
- VM vs. Container
- Containerization vs. Virtualization
- Containerized Applications
- Microservices and Containerization
- Registry Scanning
- Docker CVEs
- Docker Monitoring
- Securing Containers with Docker Scanning
- Docker CIS Benchmark
- Seccomp
- Docker Alpine
- Docker API
- Docker Tools
- 100 Best Docker Tutorials
- Docker Alternatives
- Docker Swarm
- Docker Containers vs. Virtual Machines (VMs)
- Docker Architecture
- Docker Networking
- Docker Registries
- Docker Orchestration
- OpenShift vs Docker
- Container Cloud Computing
- Container DevOps
- Docker in Production
- Container Monitoring
- Container Advantages
- Docker Hub
- Serverless Architecture
- Supply Chain Security
- Supply Chain Compliance
- SolarWinds Attack
- Supply Chain Security
- Secure Software Development Lifecycle
- Software Supply Chain Attacks
- Dependency Confusion Attack
- SLSA
- SSDF
- Software Composition Analysis
- Security Misconfigurations
- Repojacking
- Privilege Escalation
- CI/CD Security
- SAST Security
- GitLab Security
- GitHub Secret Scanning
- OWASP Dependency-Check
- Software Bill of Materials
- SBOM Tools
- NPM Vulnerabilities
- Log4j Vulnerability
- Text4Shell
- Secrets Management
- Jenkins Security
- Yarn vs. NPM
- Source Code Leaks
- Container Image Signing
- Open Source Licenses
- Vulnerability Management
- Vulnerability Management Tools
- Vulnerability Scanning Process
- Vulnerability Management
- Vulnerability Scanning
- Vulnerability Prioritization
- Open Source Vulnerability Scanning
- Vulnerability Remediation
- Vulnerability Scanner
- Risk-Based Vulnerability Management
- Vulnerability Exploitability eXchange (VEX)
- Malware Detection
- Fileless Malware
- Attack Vectors
- Malicious Code
- Risk Posture
- Alert Fatigue in Cybersecurity
- Cyber Security Posture
- MITRE ATT&CK
- MITRE ATT&CK Framework
- LLM Security
- Code Scanning
- Attack Surface
- Attack Surface Management
- What Are Indicators of Compromise (IoC)?
- Secure Code
- Configuration Drift
- Trivy
- DevSecOps
- DevSecOps
- DevSecOps Pipeline
- DevSecOps Best Practices
- DevSecOps vs SecDevOps
- Threat Modeling
- Mean Time to Repair (MTTR)
- eBPF Linux
- Cloud DevOps
- DevOps Tools
- GitOps vs DevOps
- Code Security
- Secure Code Review
- DevOps Security
- Infrastructure as Code (IaC) Security
- Infrastructure as Code DevOps
- Executive Order 14028 (U.S. Cybersecurity Executive Order)
- Open Source Security
- Shift-Left Security
- Shift Right Testing and Security
- What Is SecOps (Security Operations)?
- SecDevOps
- DevSecOps Tools
- Linux Security
- Rocky Linux
- Azure DevOps
- Cloud Security
- Cloud Security
- Cloud Security Challenges
- Cloud Security Tools
- Code to Cloud
- Cloud Protection
- Cloud Security Frameworks
- Cloud Security Standards
- Cloud Security Controls
- Cloud Security Posture Management (CSPM)
- AI Workloads
- Cloud Digital Forensics
- Cloud Computing Security Architecture
- What Is Enterprise Cloud Security?
- Virtualized Security
- CSPM Tools
- Vulnerabilities in Cloud Computing
- Top 7 Risks of Cloud Computing
- Cloud Security Assessment
- Cloud Visibility
- Cloud Governance
- Cloud Security Strategy
- Cloud Security Policy
- DFIR
- Cloud Workloads
- Public Cloud Security
- Private Cloud vs. Public Cloud
- Runtime Security
- Azure Cloud Security
- Azure Security Best Practices
- Azure Security vs. AWS Security
- AWS GovCloud: Basics & How It Compares to Azure & GCP
- S3 Security
- Cloud Misconfiguration
- Terraform Security
- Hybrid Cloud Security
- Multi-Cloud Strategy
- Agentless vs. Agent-Based Security & Monitoring
- Cloud Infrastructure Security
- Gartner CSPM
- Cloud Security Scanner
- AWS CIS Benchmark
- Cloud Configuration Management
- Cloud Workload Protection (CWP)
- Cloud Workload Protection Platforms (CWPP)
- Cloud Workload Security
- Cloud Vulnerabilities and Tools that Can Help
- Google Cloud Security
- Shared Responsibility Model
- AWS Shared Responsibility Model
- AWS Cloud Security
- Multi Cloud Security
- Cloud Compliance
- Kubernetes in Production
- Cloud Detection And Response
What Is SSDF (Secure Software Development Framework)?
The National Institute of Standards and Technology (NIST) Secure Software Development Framework (SSDF) is a set of guidelines and best practices for secure software.
What Is SSDF (Secure Software Development Framework)?
The National Institute of Standards and Technology (NIST) Secure Software Development Framework (SSDF) is a set of guidelines and best practices for designing, developing, and maintaining secure software. These typically include guidelines for secure coding, threat modeling, vulnerability management, and incident response, among other areas. They may also include specific requirements for compliance with regulatory standards or industry best practices.
The SSDF standard was created as a result of the President’s Executive Order (EO) on “Improving the Nation’s Cybersecurity (14028).” NIST created the standard to improve the cybersecurity posture of federal agency cybersecurity in line with the EO.
The goal of the SSDF is to help organizations create software that is less susceptible to security breaches and vulnerabilities. The NIST SSDF version 1.1 was produced in response to the 2021 executive order to strengthen cybersecurity across the United States. It establishes standardized terminology for software security.
This is part of a series of articles about software supply chain security.
In this article:
How Can the NIST SSDF Benefit Software Security?
The framework can benefit software security in a number of ways:
- Structure: The NIST SSDF provides a structured approach to software development that can help organizations identify and mitigate security risks throughout the development process.
- Industry standards: The NIST SSDF aligns with industry standards and best practices, so organizations can be confident that they are following established guidelines for secure software development.
- Compliance: The NIST SSDF can help organizations comply with regulatory requirements for software security, such as those imposed by the Federal Risk and Authorization Management Program (FedRAMP) and the Health Insurance Portability and Accountability Act (HIPAA).
- Risk management: The NIST SSDF provides a comprehensive framework for managing risk throughout the software development lifecycle.
- Improving the security of software: By following the NIST SSDF, organizations can improve the security of their software by identifying and addressing potential vulnerabilities and threats early in the development process.
SSDF Sections
The framework includes sections on the following objectives.
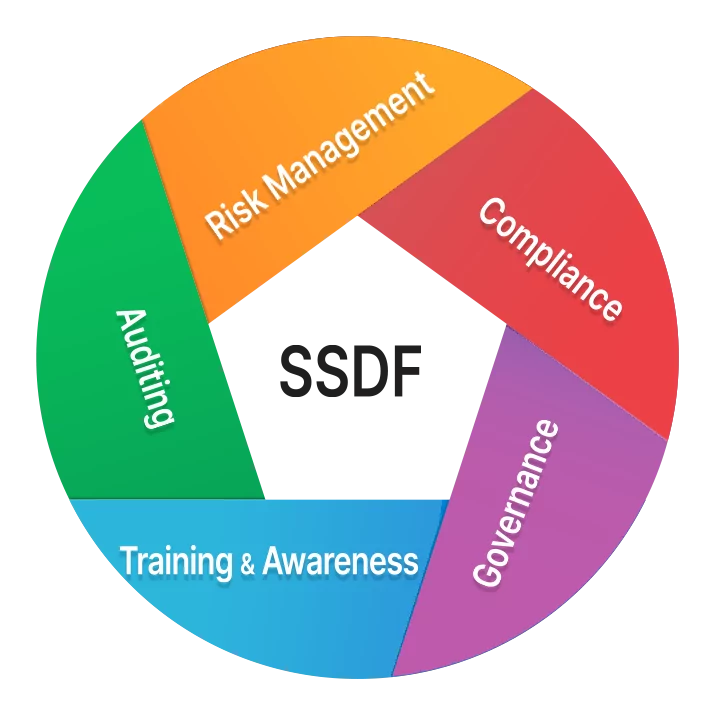
Preparation
The NIST Secure Software Development Framework (SSDF) includes a section on “Preparing the Organization” which focuses on establishing the necessary policies, procedures, and practices for secure software development. This section covers several key areas, including:
- Governance: The overall governance of software development within the organization, including roles and responsibilities, decision-making processes, and oversight of software development activities.
- Risk management: The processes and procedures for identifying, assessing, and mitigating risks throughout the software development lifecycle.
- Compliance: The requirements for compliance with relevant regulatory standards and best practices, such as those imposed by the Federal Risk and Authorization Management Program (FedRAMP) and the Health Insurance Portability and Accountability Act (HIPAA).
- Training and awareness: The training and awareness programs that need to be in place to ensure that all software development personnel are aware of the organization’s secure software development policies and procedures, and are equipped to develop software in accordance with those policies and procedures.
- Auditing: The processes and procedures for auditing software development activities to ensure that they are in compliance with the organization’s secure software development policies and procedures.
Protection
The SSDF includes a section on “Protecting the Software” which focuses on the technical measures and controls that organizations can use to protect their software. This section covers several key areas, including:
- Secure coding: The principles and practices of secure coding, including best practices for writing secure code, identifying and addressing common vulnerabilities, and testing for security.
- Threat modeling: The process of identifying, assessing, and mitigating potential threats to the software.
- Vulnerability management: The process of identifying, assessing, and mitigating known vulnerabilities in the software.
- Incident response: The planning and preparation for responding to security incidents, including incident response procedures and incident response teams.
- Security testing: The different types of security testing that should be performed on software, such as penetration testing, vulnerability scanning, and security code reviews.
Secure Software Production
The SSDF includes a section on “Producing Well-Secured Software” which focuses on the processes and procedures for developing software in a secure manner. This section covers several key areas, including:
- Secure software development life cycle (SDLC): The secure software development life cycle, which includes the phases of software development and the security-related activities that should be performed during each phase.
- Secure requirements: The process of gathering and defining secure software requirements and how to ensure that the requirements align with the organization’s security policies and standards.
- Secure design: The process of designing secure software and the design principles that should be followed to ensure that the software is secure. The software settings must be secure by default.
- Secure implementation: The process of implementing secure software and the best practices for writing secure code.
- Secure verification: The process of verifying that the software is secure and the different types of security testing that should be performed on software.
- Secure deployment: The process of deploying secure software and the security-related activities that should be performed before, during, and after deployment.
Vulnerability Response
The NIST SSDF includes guidance on responding to vulnerabilities in software systems. The framework advises organizations to establish a vulnerability management process that includes the following steps:
- Identification: Detecting and identifying vulnerabilities in software systems, including through the use of tools such as vulnerability scanners and penetration testing.
- Prioritization: Assessing the risk posed by each vulnerability, taking into account factors such as the likelihood of exploitation and the potential impact.
- Remediation: Developing and implementing a plan to address the vulnerabilities, including patching or upgrading software, implementing workarounds, or taking other steps to mitigate the risk.
- Verification: Testing and validating that the vulnerabilities have been successfully addressed.
- Communication: Communicating vulnerabilities and remediation actions to stakeholders, including customers, partners, and other interested parties.
The framework also recommends that organizations establish an incident response plan to handle security incidents and vulnerabilities that cannot be addressed through the vulnerability management process.
- Supply Chain Compliance: 4 Standards You Should Know
- SolarWinds Attack: Play by Play and Lessons Learned
- Supply Chain Security: Mitigating the Supply Chain Threat
- What Is the Secure Software Development Lifecycle (SSDLC)?
- Software Supply Chain Attacks: 6 Examples and 6 Defensive Strategies
- Dependency Confusion Attack
- What Is SLSA and How to Use it for Supply Chain Security
- What Is Software Composition Analysis (SCA)?
- Security Misconfiguration: Types, Examples & Prevention Tips
- Why Repojacking Is a New Mega Threat & Protecting Your Projects
- Privilege Escalation in Windows, Linux, and K8s and 6 Ways to Prevent It
- CI/CD Security: Threats, Tools, and Best Practices
- SAST Security: Is SAST Still Relevant for Modern Applications?
- GitLab Security
- GitHub Secret Scanning
- How to Analyze the OWASP Dependency-Check?
- SBOM (Software Bill of Materials)
- What Are SBOM Tools?
- 6 Common npm Vulnerabilities and How to Fix Them
- Log4j Vulnerability: Updated Info and Protection for 2023
- Text4Shell CVE (CVE-2022-42889): Impact and Fixes
- What Is Secrets Management? Challenges and Best Practices
- Jenkins Security: How it Works & Best practices
- Yarn vs. NPM: Which Package Manager You Should Choose, and Why?
- Source Code Leaks: How to Avoid Them Before They Happen
- Container Image Signing: A Practical Guide
- 5 Open Source Licenses and Compliance Risks to Know About
- Show more
Aqua Cloud Native Application Protection Platform (CNAPP)
Go cloud native with the experts!