What Is Application Security Posture Management (ASPM)?
Application security posture management (ASPM) is an agile AppSec delivery model that helps organizations effectively manage their application security posture.
Application security posture management (ASPM) is an agile application security (AppSec) delivery model, which helps organizations manage the security posture of their critical applications. It helps organizations to establish a sustainable AppSec program by providing a comprehensive and continuous approach to application security.
ASPM enables organizations to prioritize, automate, and govern their assets and close the gap between security and vulnerabilities. This approach helps organizations to identify and address security issues early in the development cycle, which reduces the risk of security incidents and ensures that applications are secure and safe to use.
In this article:
- What Are the Benefits of ASPM?
- Key Capabilities of ASPM
- ASPM vs. CSPM: What Is the Difference?
- Application Security Posture Management Best Practices
- Implement a Continuous Security Testing Program
- Establish Secure Coding Guidelines
- Implement a Secure Deployment Process
- Regularly Review and Update Application Security Policies
- Provide Security Training for Developers
- Establish a Strong Incident Response Plan
What Are the Benefits of ASPM?
ASPM solutions offer a range of benefits to organizations looking to manage their application security posture effectively, including:
- Data collection: ASPM solutions can collect different types of data about an organization’s applications, including metadata, configuration data, and code-level information. This information is useful for informing strategic corporate security and vulnerability management decisions, helping security teams to identify and address security issues more effectively.
- Risk visibility: An ASPM solution can automatically perform vulnerability scanning and collect data on AppSec risks. The contextualized risk information can be useful for prioritizing remediation operations and maximizing the effectiveness of the organization’s vulnerability management strategy.
- Rapid remediation: ASPM solutions enable security teams to address vulnerabilities quickly after they have been discovered or introduced into a corporate application.
- Data security: An ASPM solution can map the flow of data between an organization’s applications, making it easier for the security team to enforce access controls based on least privilege principles and remediate potential risks to data security. This helps to ensure that sensitive data is protected and that data breaches are prevented.
Key Capabilities of ASPM
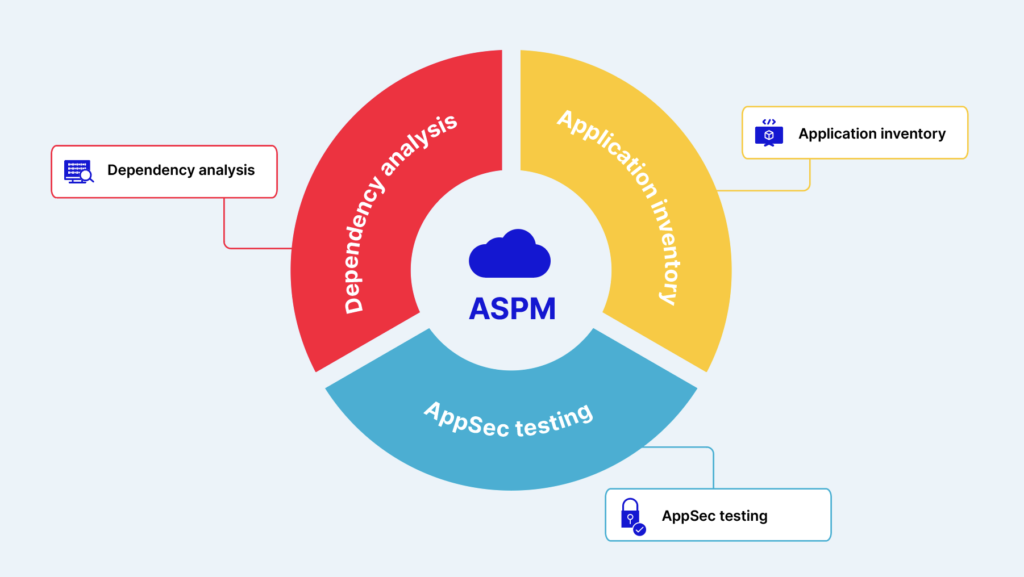
An ASPM solution is designed to automate and streamline the application security pipeline in an organization’s environment. These solutions typically offer capabilities such as:
- Application inventory: ASPM solutions can automatically identify and list the organization’s applications, including those dispersed across different on-premises and cloud-hosted platforms. This helps organizations to gain visibility into their application portfolio and prioritize their security efforts accordingly.
- AppSec testing: ASPM solutions offer a range of application security testing capabilities, such as SAST (static application security testing), DAST (dynamic application security testing), SCA (software composition analysis), and vulnerability scanning. These tools orchestrate and automate security tests to provide continuous visibility across multiple security risks, ensuring development and security teams can address vulnerabilities in a timely manner.
- Dependency analysis: An ASPM solution can map data flows and dependencies within an organization’s application portfolio. This capability enables ASPM tools to visualize the structure and makeup of the corporate application environment, providing insights into potential risks and vulnerabilities.
ASPM vs. CSPM: What Is the Difference?
ASPM and CSPM are two different but complementary approaches to managing an organization’s security posture.
What is CSPM?
CSPM, or cloud security posture management, is a cloud security model that focuses on identifying and mitigating risks in cloud environments. CSPM solutions provide security teams with visibility into their cloud infrastructure, identifying security misconfigurations, compliance issues, and potential risks. CSPM solutions can enforce security policies across multiple cloud environments, making it easier to maintain a consistent security posture.
Comparing ASPM to CSPM
| ASPM | CSPM | |
| Focus | Application security | Cloud Security |
| Objective | To identify and remediate vulnerabilities | To identify and mitigate risks in cloud infra |
| Scope | Application portfolio | Cloud infrastructure |
| Key features | Automated security testing, vulnerability scanning, dependency analysis, data security | Visibility into cloud infrastructure, risk identification, compliance monitoring, policy enforcement |
| Benefits | Rapid remediation of vulnerabilities, data security, comprehensive and continuous approach to AppSec | Improved visibility, risk mitigation, policy enforcement, compliance monitoring |
| Use cases | Agile software development, DevOps, cloud-based applications | Cloud environments, multi-cloud deployments, compliance monitoring |
| Key challenges | Balancing security and agility in software development, managing application portfolios across multiple environments | Ensuring visibility across multiple cloud environments, managing security across different cloud service providers |
While ASPM and CSPM each have a different focus, they are complementary approaches to security management. ASPM helps organizations to identify and remediate vulnerabilities in their applications, while CSPM helps organizations to identify and mitigate risks in their cloud infrastructure. Together, these approaches help organizations to maintain a strong security posture and protect their assets from potential threats.
Application Security Posture Management Best Practices
Implement a Continuous Security Testing Program
A continuous security testing program involves the use of automated security testing tools, such as dynamic and static application security testing, to continuously scan applications for vulnerabilities and security flaws. This helps identify vulnerabilities early in the development process, reducing the risk of security breaches. The program should include regular vulnerability scans and penetration testing, as well as monitoring of production systems.
Establish Secure Coding Guidelines
Secure coding guidelines should be established and followed throughout the development lifecycle to ensure that applications are designed and coded securely. These guidelines should cover areas such as input validation, authentication, and access control. Guidelines should be based on industry best practices and should be reviewed regularly to ensure they remain up-to-date.
Implement a Secure Deployment Process
A secure deployment process involves the use of tools and processes that help ensure that applications are deployed securely. This includes practices such as containerization, virtual patching, and the use of secure configurations. The deployment process should include security checks and testing to ensure that no vulnerabilities are introduced during the deployment process.
Regularly Review and Update Application Security Policies
Application security policies should be reviewed and updated regularly to ensure that they remain relevant and effective. This includes policies related to secure coding, secure deployment, incident response, and data protection. Policies should be based on industry best practices and should be reviewed and updated at least annually.
Provide Security Training for Developers
Security training should be provided for developers to ensure that they have the skills and knowledge necessary to design and code applications securely. This includes training on secure coding practices, vulnerability scanning, and incident response. Training should be provided regularly and should be updated as new threats emerge.
Establish a Strong Incident Response Plan
An incident response plan should be established and tested regularly to ensure that it is effective in the event of a security breach. The plan should include procedures for identifying, containing, and remediating security incidents, as well as processes for communicating with stakeholders and reporting incidents to regulatory authorities. The plan should be reviewed and updated at least annually and should include regular testing and training to ensure that it remains effective.
Aqua Cloud Native Application Protection Platform (CNAPP)
Go cloud native with the experts!