Zero Day Attack
What Are Zero Day Attacks?
A zero-day attack, also known as a zero-day vulnerability, is a type of cyberattack that takes advantage of a previously unknown vulnerability in a computer system, application, or network. These types of attacks are particularly dangerous because they can be launched without the knowledge of the affected parties and can be very difficult to detect and prevent.
The term “zero-day” refers to the fact that the vulnerability being exploited has not yet been discovered or publicly disclosed. This means that there are no patches or fixes available to protect against it, and the affected parties may not even be aware that the vulnerability exists.
Zero-day attacks can be used to steal sensitive information, disrupt services, or install malicious software on a victim’s system. They are often used by cybercriminals and nation-state hackers to carry out espionage or sabotage.
To protect against zero-day attacks, it is important to regularly update software and systems, implement strong security protocols, and be vigilant about detecting and responding to unusual activity.
This is part of a series of articles about cloud attacks.
In this article:
How Are Zero-Day Attacks Carried Out?
Zero-day attacks are typically executed by finding and exploiting a previously unknown vulnerability in a computer system, application, or network. This can be done in a number of ways, such as by:
- Scanning for vulnerabilities: Hackers can use specialized software to scan networks and systems for vulnerabilities that can be exploited.
- Reverse engineering: Hackers can reverse engineer software or hardware to find vulnerabilities that can be exploited.
- Social engineering: Hackers can use social engineering techniques, such as phishing or baiting, to trick individuals into revealing sensitive information or installing malicious software.
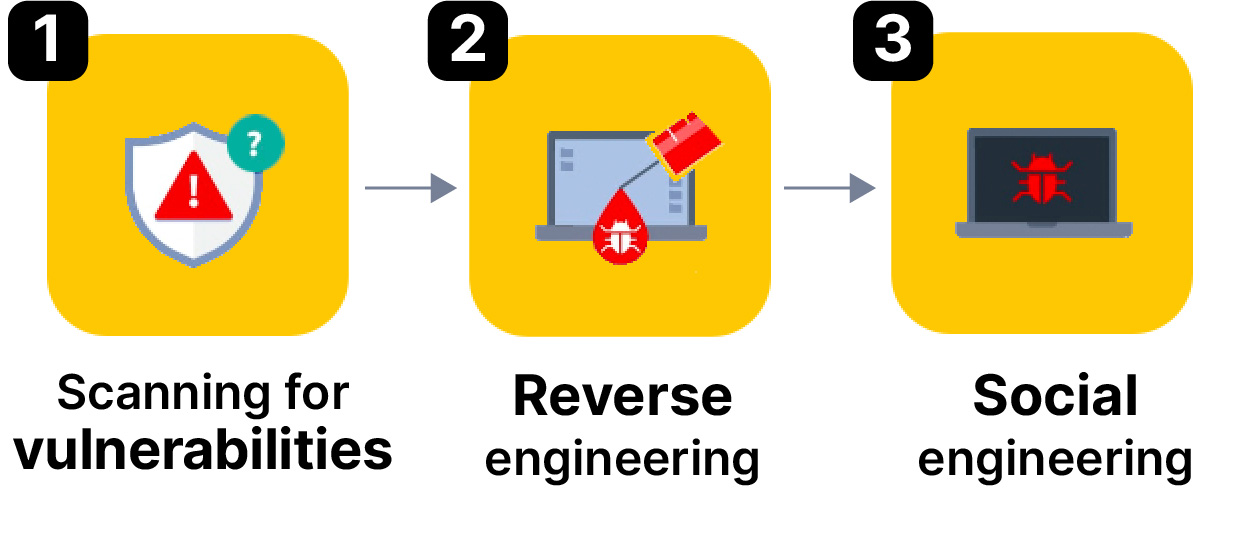
Once a zero-day vulnerability has been discovered, the attacker can use it to launch an attack on the affected system or network. This can have serious consequences for the affected parties, including the loss of sensitive data, disruption of services, and damage to reputation.
For vendors and companies, zero-day attacks can be especially damaging because they may not be aware that a vulnerability exists until it has been exploited. This can make it difficult to quickly patch the vulnerability and prevent further attacks.
How to Detect a Zero-Day Attack
Zero-day exploits are a significant challenge for organizations because they take advantage of unknown vulnerabilities in software, which means that traditional security measures may not be effective at detecting or preventing them. This makes it difficult for organizations to protect themselves against these types of attacks.
Here are strategies that organizations can use to detect zero-day attacks:
- Signature-based detection: identifying specific patterns or “signatures” in software or network traffic that are indicative of a zero-day exploit. This can be effective at detecting known zero-day exploits, but it may not be effective at detecting unknown or novel zero-day exploits.
- Behavior-based monitoring: monitoring the behavior of software and systems to identify unusual or suspicious activity that could indicate a zero-day exploit. This can be effective at detecting both known and unknown zero-day exploits, but it can also generate a high number of false positives.
- Hybrid detection methods: combine two or more of these approaches in an effort to improve the effectiveness of zero-day exploit detection. These methods may involve combining signature-based detection with behavior-based monitoring, for example, in order to improve accuracy and reduce the number of false positives.
It is important for organizations to have multiple layers of defense in place to protect against zero-day exploits, as no single approach is foolproof. Regular software updates and patches, along with robust network and system monitoring, can help organizations to stay one step ahead of these types of attacks.
Preventing Zero Days: Basic Measures
Detection of a zero-day attack can be challenging because the attack takes advantage of a previously unknown vulnerability. However, there are a few steps that organizations can take to help detect and prevent zero-day attacks:
- Patch vulnerabilities promptly: Regularly updating systems and software can help prevent zero-day attacks by closing known vulnerabilities.
- Implement strong security protocols: Implementing strong security protocols, such as firewalls, intrusion detection systems, and two-factor authentication, can help protect against zero-day attacks by limiting the ability of attackers to access sensitive information or systems.
- Monitor for unusual activity: Regularly monitoring for unusual activity, such as unusual network traffic or suspicious logins, can help detect potential zero-day attacks.
- Train employees on security best practices: Training employees on security best practices, such as avoiding suspicious emails and links, can help prevent zero-day attacks that rely on social engineering techniques.
- Work with security experts: Working with security experts or consulting firms can provide valuable insights and help organizations stay up to date on the latest threats and vulnerabilities.
The key to detecting and preventing zero-day attacks is to be proactive about security and constantly vigilant for unusual activity.
Preventing Zero Days: 4 Advanced Defensive Measures
1. Code Scanning
Code scanning tools work by automatically analyzing the source code of a program or application for vulnerabilities and security flaws. Here are several best practices to consider:
- Implement code scanning tools: There are a variety of code scanning tools available that can help identify vulnerabilities in your systems and software. These tools can be configured to scan your code on a regular basis and alert you to any potential vulnerabilities.
- Regularly scan your code: To effectively protect against zero-day attacks, it is important to regularly scan your code for vulnerabilities. This can help ensure that any vulnerabilities are discovered and addressed before they can be exploited by attackers.
- Fix identified vulnerabilities: When code scanning tools identify vulnerabilities, it is important to promptly fix them to prevent zero-day attacks. This can involve applying patches or making code changes to address the vulnerability.
- Test code changes: Before deploying code changes, it is important to thoroughly test them to ensure that they do not introduce new vulnerabilities or disrupt the functionality of your systems and software.
2. Implement Patch Management
Patch management is the process of identifying, testing, and installing patches or updates to software and systems in order to fix vulnerabilities and improve security. It is an important aspect of cyber security and can be an effective way to protect against and prevent zero-day attacks.
Here are a few steps organizations can take to use patch management to protect against zero-day attacks:
- Implement patch management processes: Establishing patch management processes and procedures can help ensure that vulnerabilities are promptly identified and addressed. This can include regularly checking for and installing updates, as well as testing patches before deploying them to production systems.
- Automate patch management: Automating patch management can help ensure that patches are applied promptly and consistently across all systems and devices. This can involve using specialized patch management software or integrating patch management into your existing IT infrastructure.
- Test patches before deployment: It is important to thoroughly test patches before deploying them to production systems to ensure that they do not introduce new vulnerabilities or disrupt the functionality of your systems and software.
- Train employees on patch management: Training employees on patch management processes and procedures can help ensure that patches are applied promptly and consistently across all systems and devices.
3. Threat Modeling
Threat modeling is the process of identifying and assessing potential threats to a system or organization. Here are a few steps organizations can take to use threat modeling to protect against zero-day attacks:
- Identify potential threats: The first step in threat modeling is to identify potential threats to your systems and data. This can include threats that are specific to your organization, as well as more general threats that are common across different types of organizations.
- Assess the likelihood and impact of potential threats: Once potential threats have been identified, it is important to assess the likelihood and impact of each threat. This can help prioritize efforts to mitigate the most significant threats.
- Develop strategies to mitigate identified threats: Based on the likelihood and impact of identified threats, organizations can develop strategies to mitigate them. This can include implementing security measures such as fifrewalls, intrusion detection systems, and two-factor authentication, as well as establishing incident response plans and training employees on security best practices.
- Regularly review and update threat models: Threat models should be regularly reviewed and updated to ensure that they accurately reflect the current state of the organization and its systems. This can help ensure that the organization is prepared to handle new or emerging threats.
4. Zero Trust
Zero trust is a cybersecurity concept that involves adopting a “never trust, always verify” approach to security. In a zero trust environment, all network traffic is treated as potentially malicious, and access to resources is based on strict access controls and continuous verification of user and device identity.
Here are a few steps organizations can take to use zero trust to protect against zero-day attacks:
- Implement strict access controls: In a zero trust environment, access to resources is based on strict access controls. This can involve using authentication and authorization methods such as two-factor authentication and multi-factor authentication to verify user and device identity.
- Monitor and control network traffic: In a zero trust environment, all network traffic is treated as potentially malicious. This can involve using tools such as firewalls and intrusion detection systems to monitor and control network traffic, and blocking or quarantining suspicious traffic.
Use micro-segmentation: Micro-segmentation is a security technique that involves dividing a network into smaller segments based on specific application or workload needs. This can help prevent zero-day attacks by limiting the impact of a potential attack to a specific segment of the network.
Aqua Cloud Native Application Protection Platform (CNAPP)
Go cloud native with the experts!